Make hidden threats visible
PT Network Attack Discovery
Overview
PT Network Attack Discovery is a network detection and response (NDR/NTA) system for detecting attacks on the perimeter and inside your network. The system makes hidden threats visible, detects suspicious activity even in encrypted traffic, and helps investigate incidents.
PT Network Attack Discovery 12.1 offers a 3x increase in indexing speed
The traffic analysis system from Positive Technologies has increased its ability to handle peak loads without requiring additional hardware
Detects malicious activities in east/west traffic
PT NAD analyzes both north/south and east/west traffic and detects lateral movement, attempts to exploit vulnerabilities, and attacks against end users on the domain and internal services.
How PT NAD maps to MITRE ATT&CK
Learn how the network detection and response system PT Network Attack Detection can identify 117 adversary techniques described in MITRE ATT&CK.
PT NAD detects
Detects even modified malware
PT NAD alerts about all dangerous threats and detects even modified versions of malware. To describe the full range of cyberthreats, our experts constantly explore the latest malware samples and hacker tools, techniques, and procedures. Each rule they create covers an entire malware family.
Positive Technologies - a Leader in XDR
Positive Technologies with its comprehensive platform has received strong ratings across technology excellence and customer impact in QKS Group SPARK Matrix.
How it works
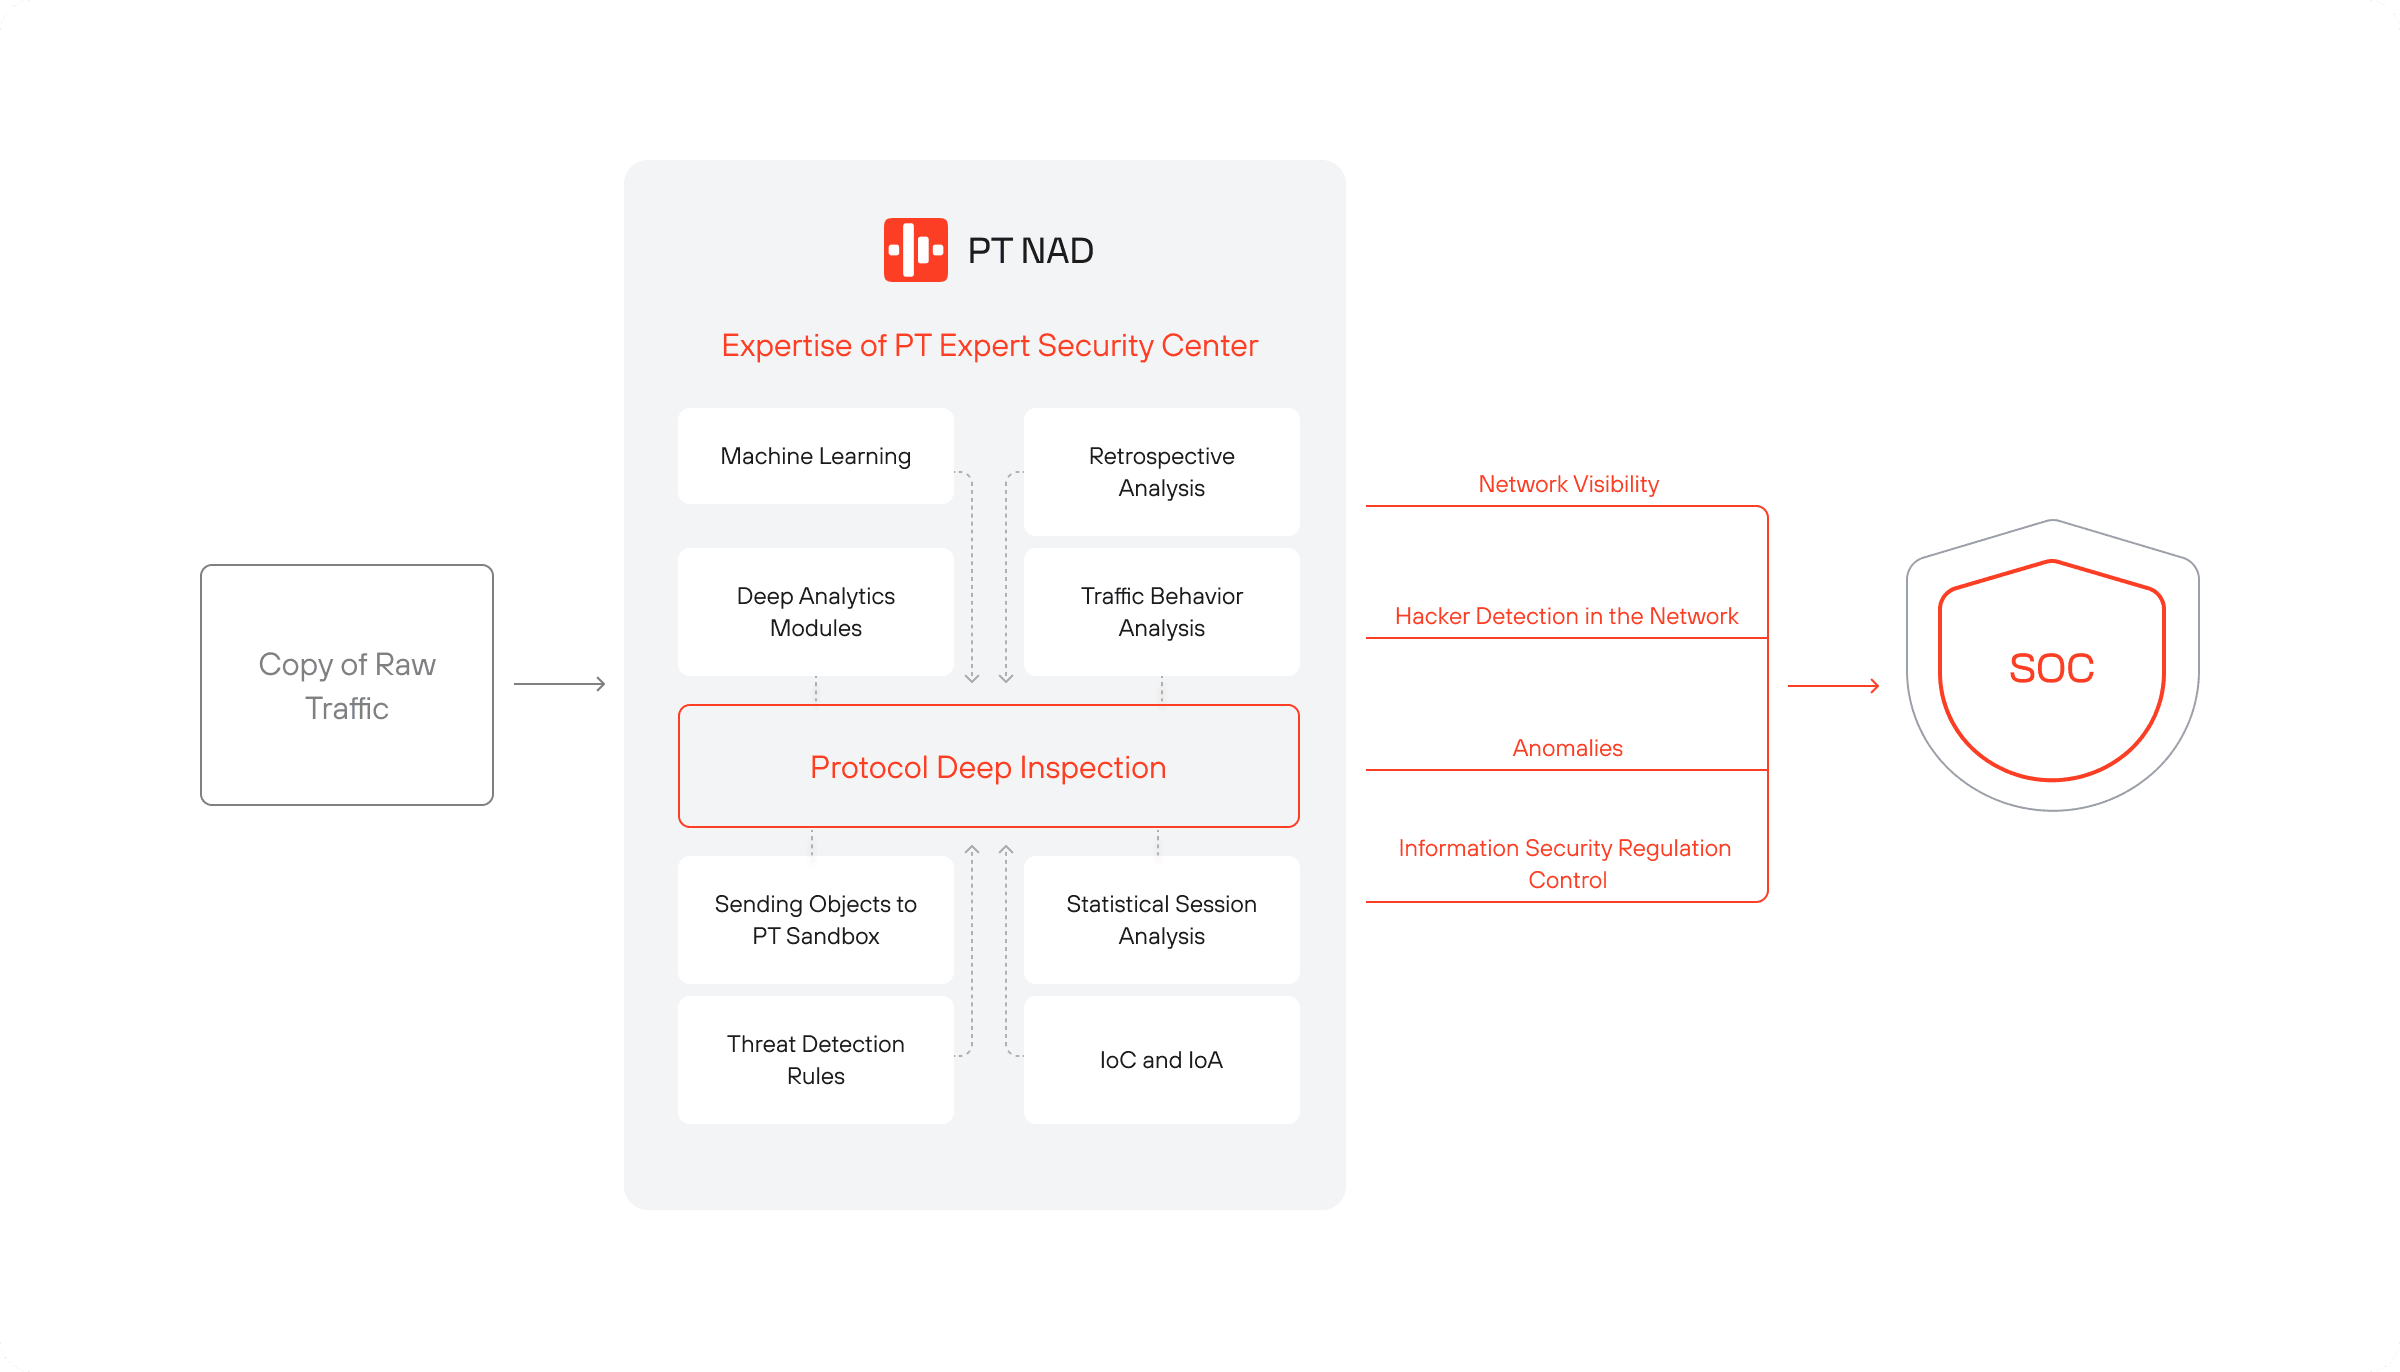
PT NAD captures and analyzes traffic on the perimeter and inside infrastructure. This allows for the detection of hacker activity at the earliest stages of network penetration, as well as during attempts to gain a foothold on the network and develop the attack.
Confidential
PT NAD is an on-premise solution. All data is stored on client infrastructure, never leaving the corporate perimeter. Information on attacks and damage is not transmitted to the outside, minimizing reputational risks.
Use scenarios
Security policy compliance
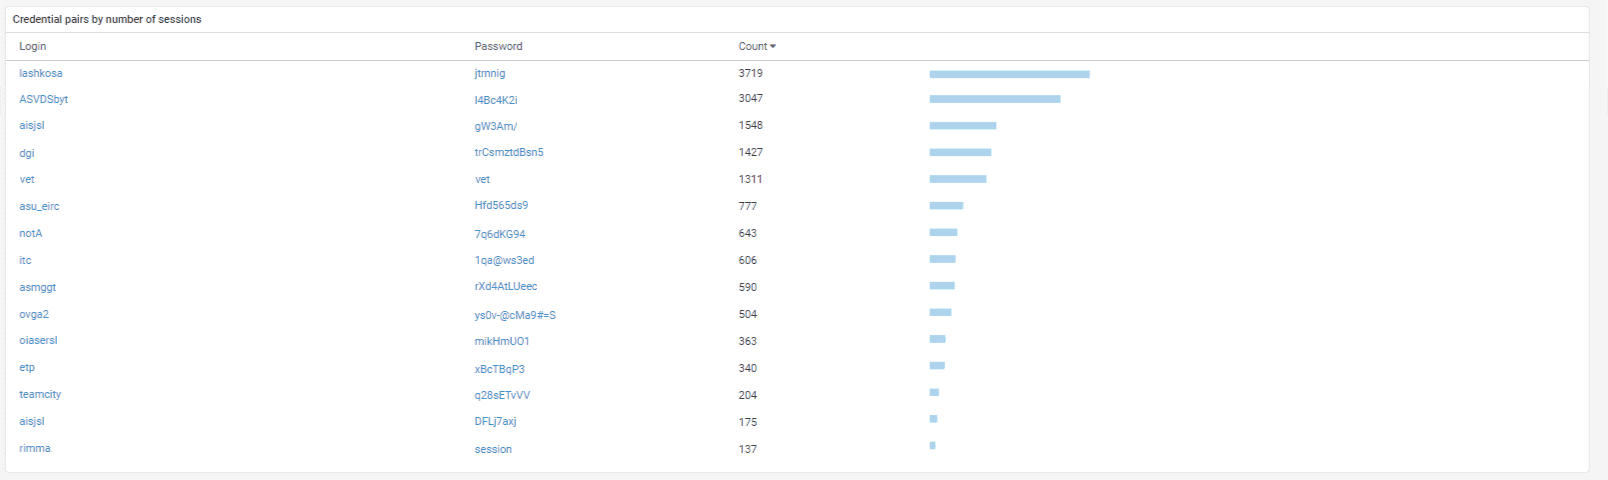
PT NAD detects IT configuration flaws and cases of non-compliance with security policies, which otherwise can offer attackers a way in. Filters help to quickly identify credentials stored in cleartext, weak passwords, remote access utilities, and tools that hide network activity. You can pin filters of interest in a separate widget for quick reference. Here is an example of a widget displaying all non-encrypted passwords:
Detection of attacks on the perimeter and inside the network
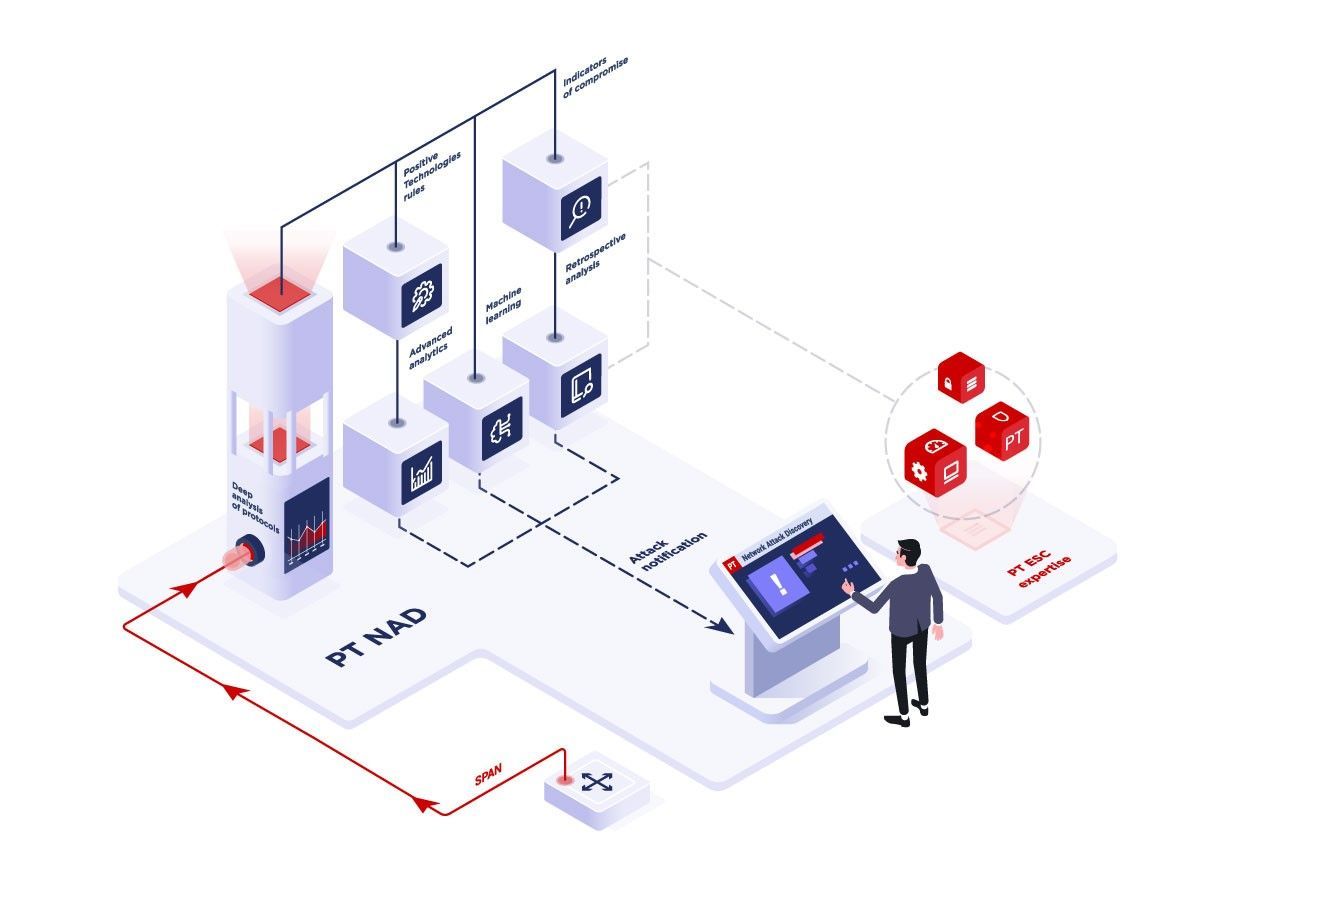
Thanks to embedded machine learning technologies, advanced analytics, unique threat detection rules, indicators of compromise, and retrospective analysis, PT NAD detects attacks both at the earliest stages and after attackers have already burrowed into infrastructure.
The PT Expert Security Center updates rules and indicators of compromise twice a week. Updating the database does not require a constant connection to the Positive Technologies cloud.
Advanced analytics modules enable identification of complex threats and network anomalies. They take into account many parameters of the attacker’s behavior and are not tied to the analysis of individual sessions, unlike the rules for attack detection.
Investigation of attacks
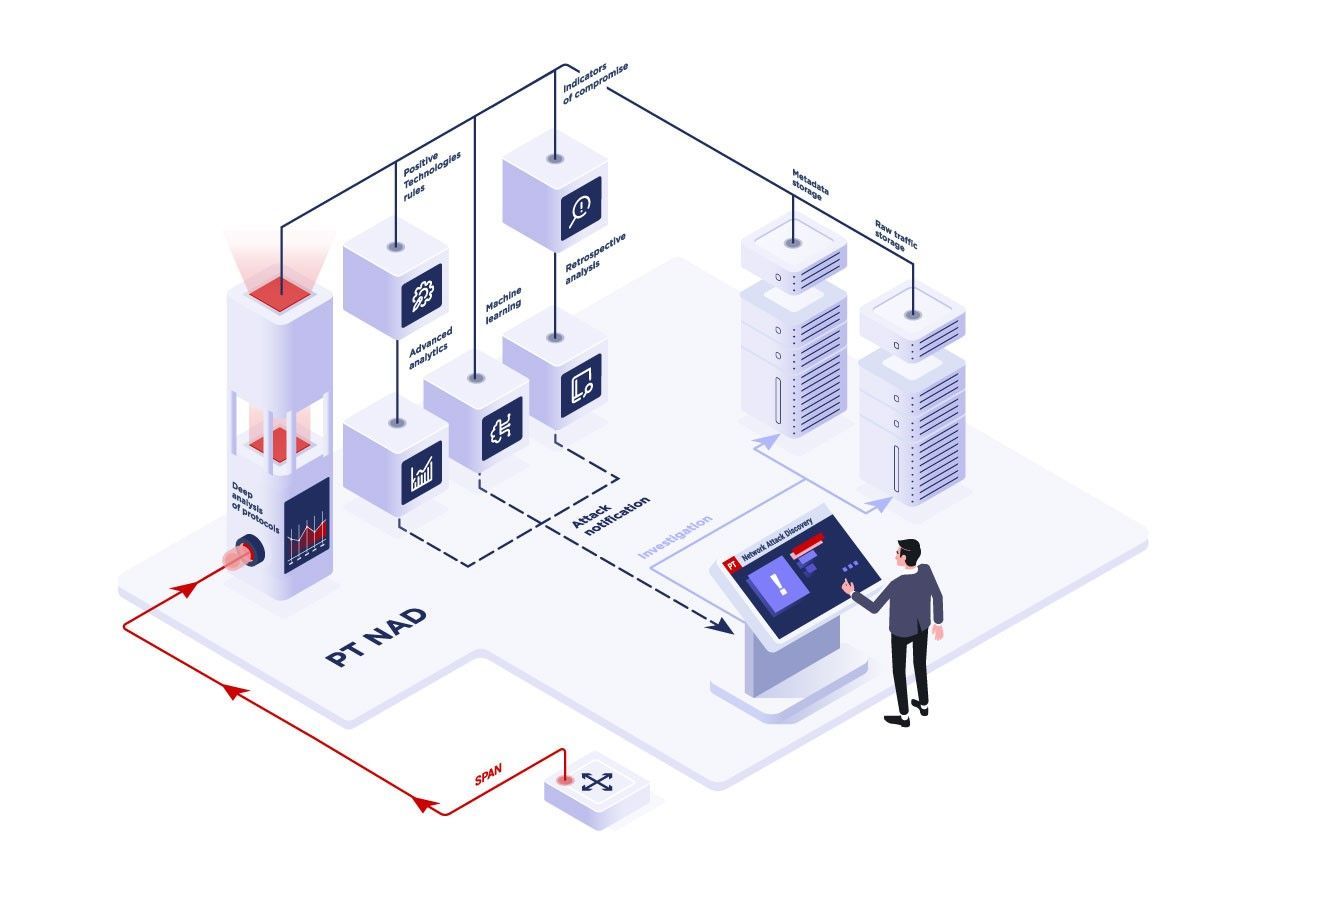
Because PT NAD saves copies of raw traffic and session data, forensic investigators can:
- Localize attacks.
- Reconstruct kill chains.
- Detect vulnerabilities in infrastructure.
- Take measures to prevent similar attacks.
- Gather evidence of malicious activity.
Threat hunting
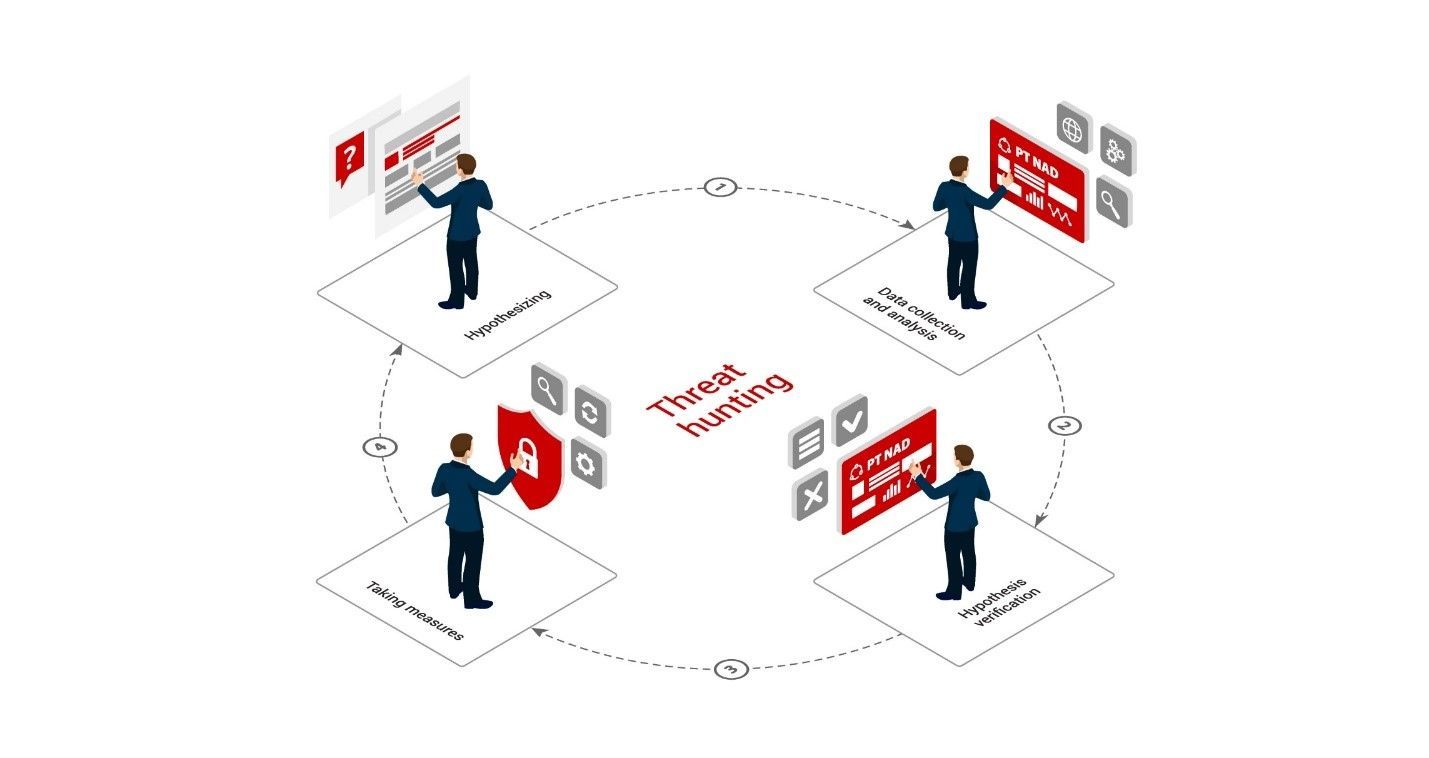
PT NAD is ideal for threat hunting and detecting hidden threats that standard cybersecurity tools miss. A security analyst with the necessary skills and infrastructure-specific knowledge can use PT NAD to empirically test hypotheses. This makes it possible to determine whether a hacker group, insider threat, or data breach is truly present, and if the hypothesis is confirmed, take proactive measures accordingly.
Key features
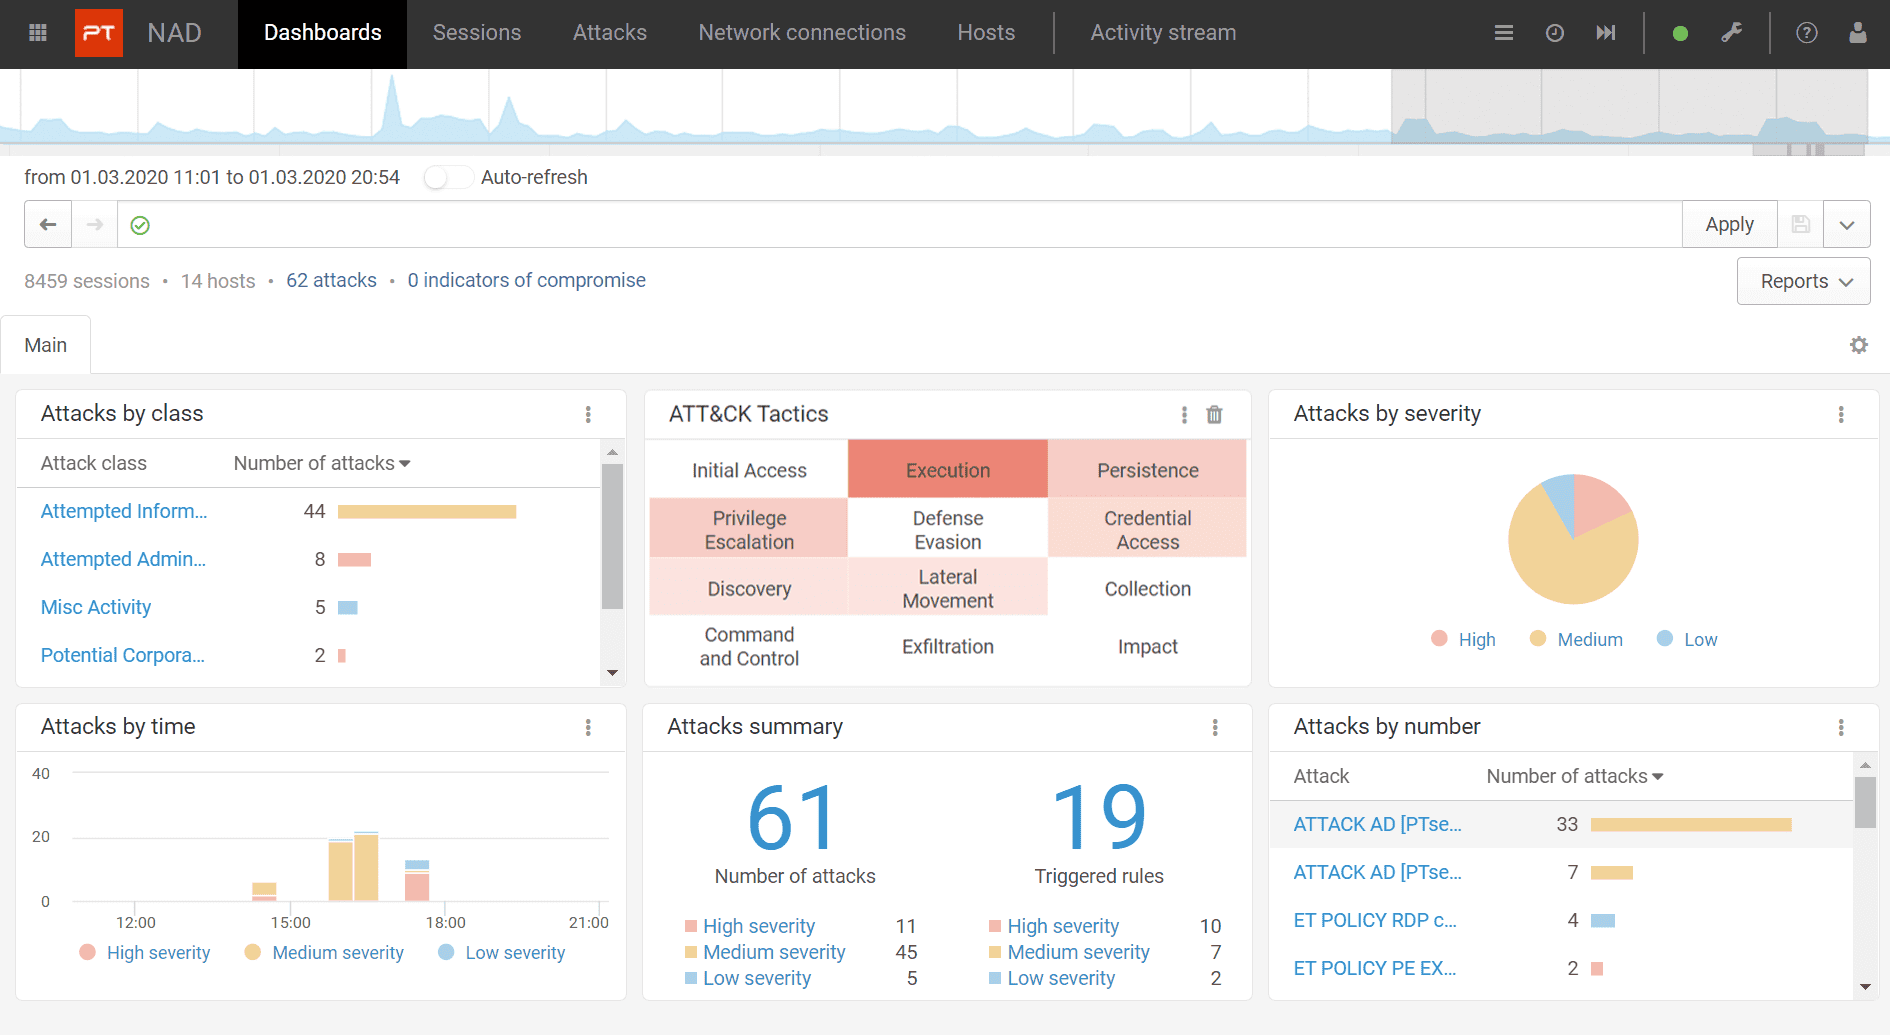
Attack detection
The system informs of incidents and automatically assesses how dangerous they are. The dashboard provides key information about all attacks: how many, which types, the degree of danger, and when they occurred. Click to view details for any attack.
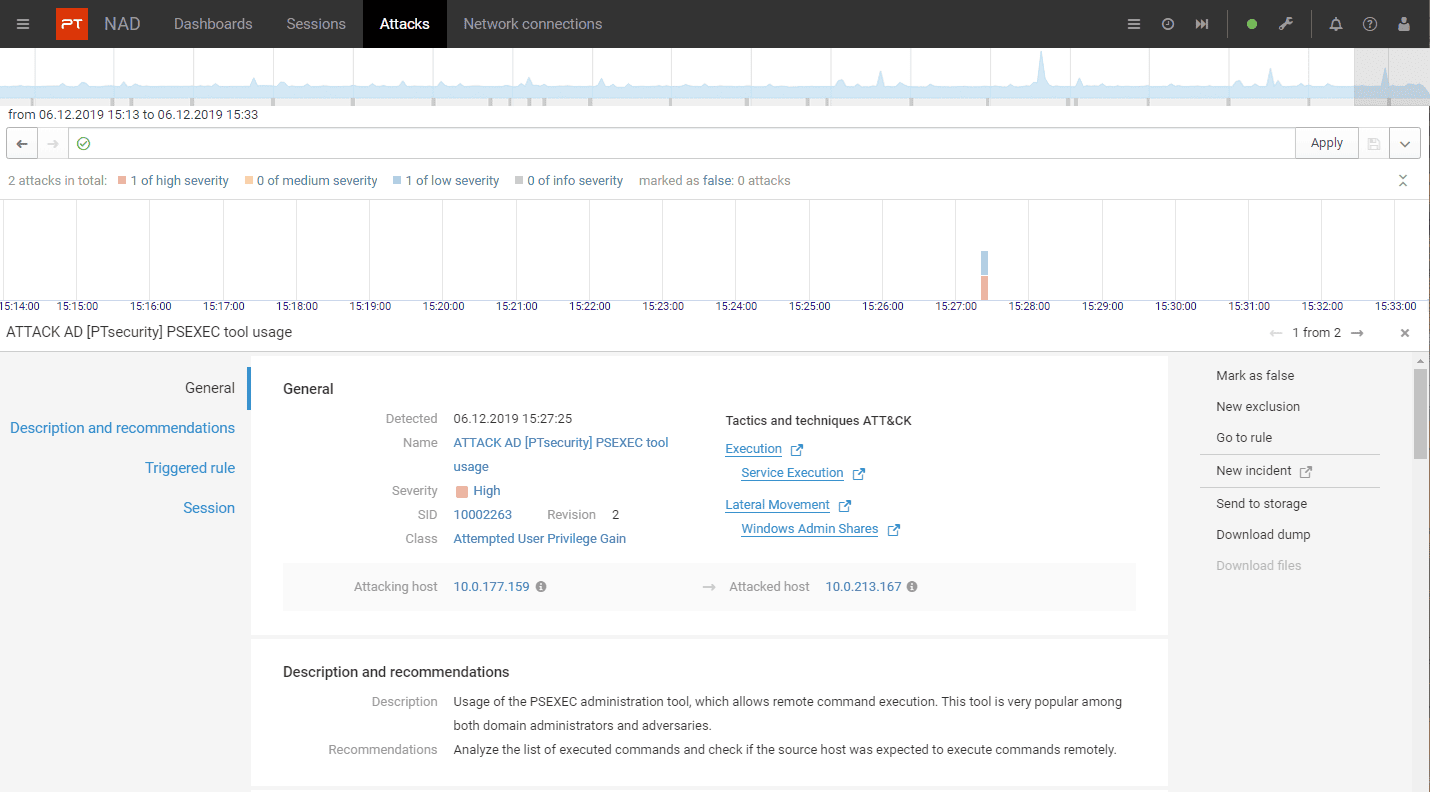
Response at a glance
Information for each attack shows the affected hosts, event time, session data, and hacker tools, techniques, and procedures (TTPs) per the MITRE ATT&CK classification. With attack staging information, you can take the right surgical measures to get the job done.
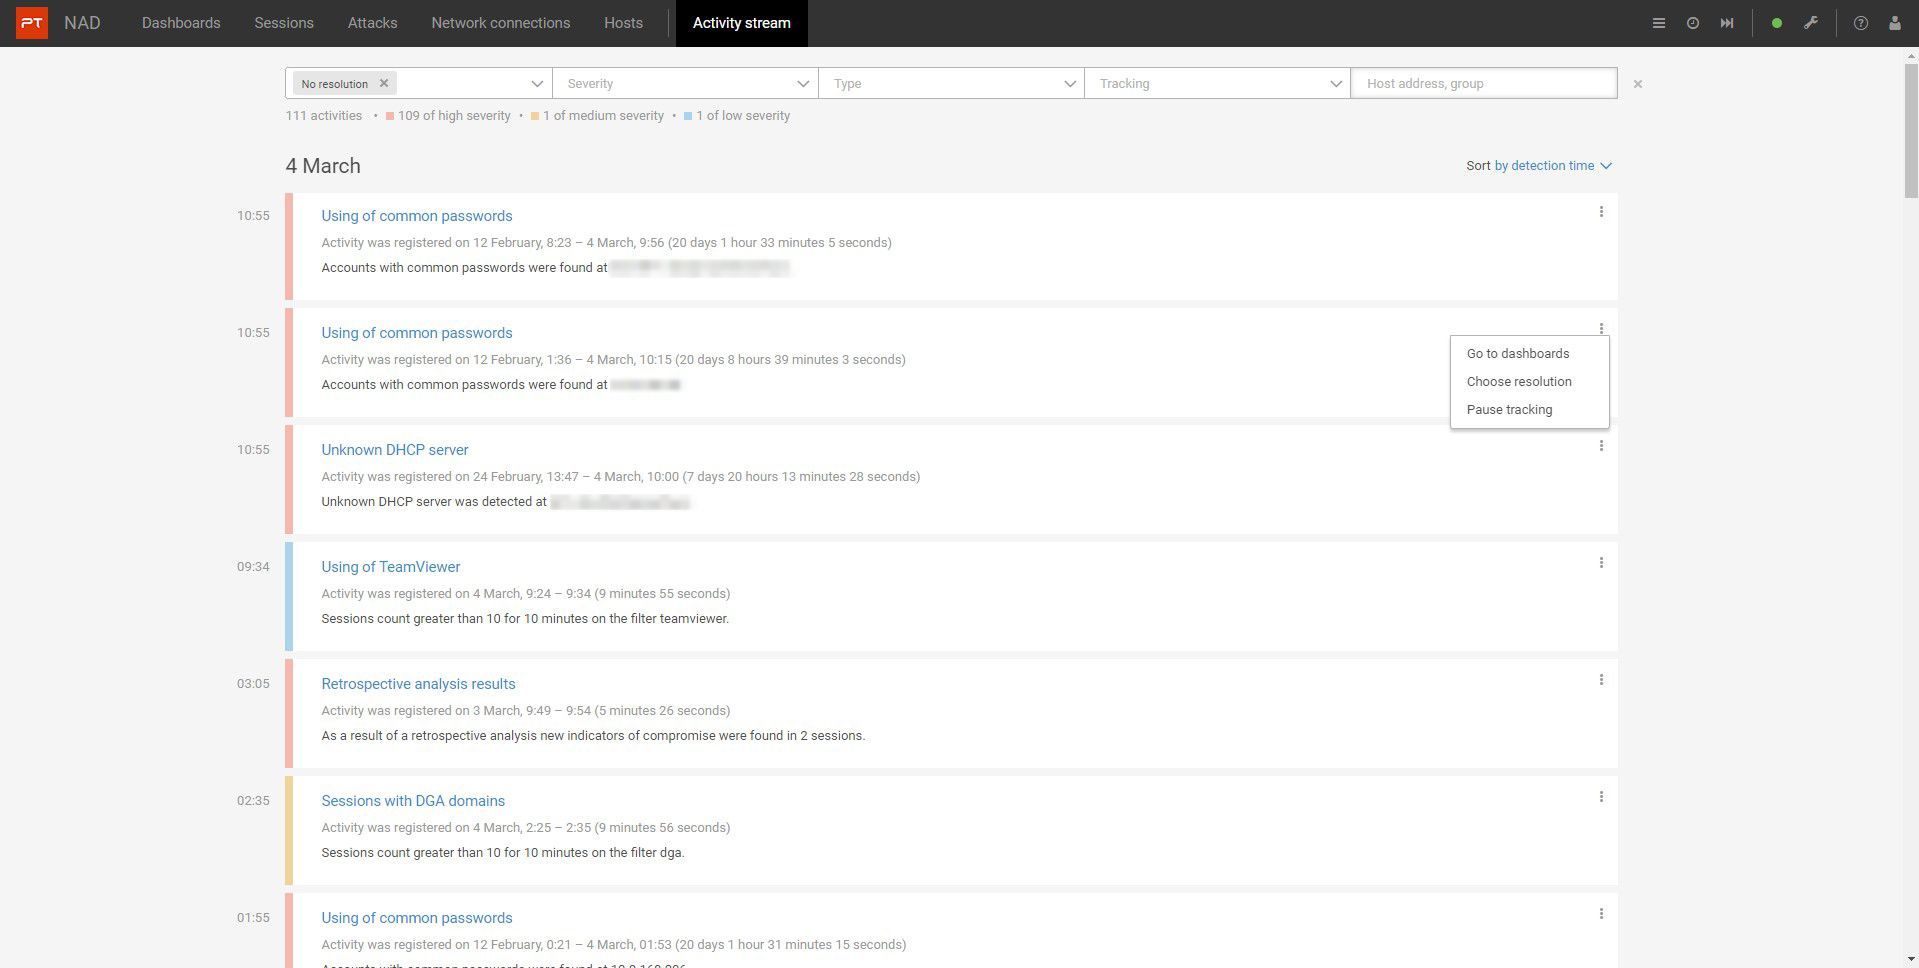
Learn about new attacks and threats in a single feed
Activity feed collects a list of identified threats in one place, combines messages about similar activities into one, and allows you to manage them. You can mark the issue as resolved or no longer track such activity.
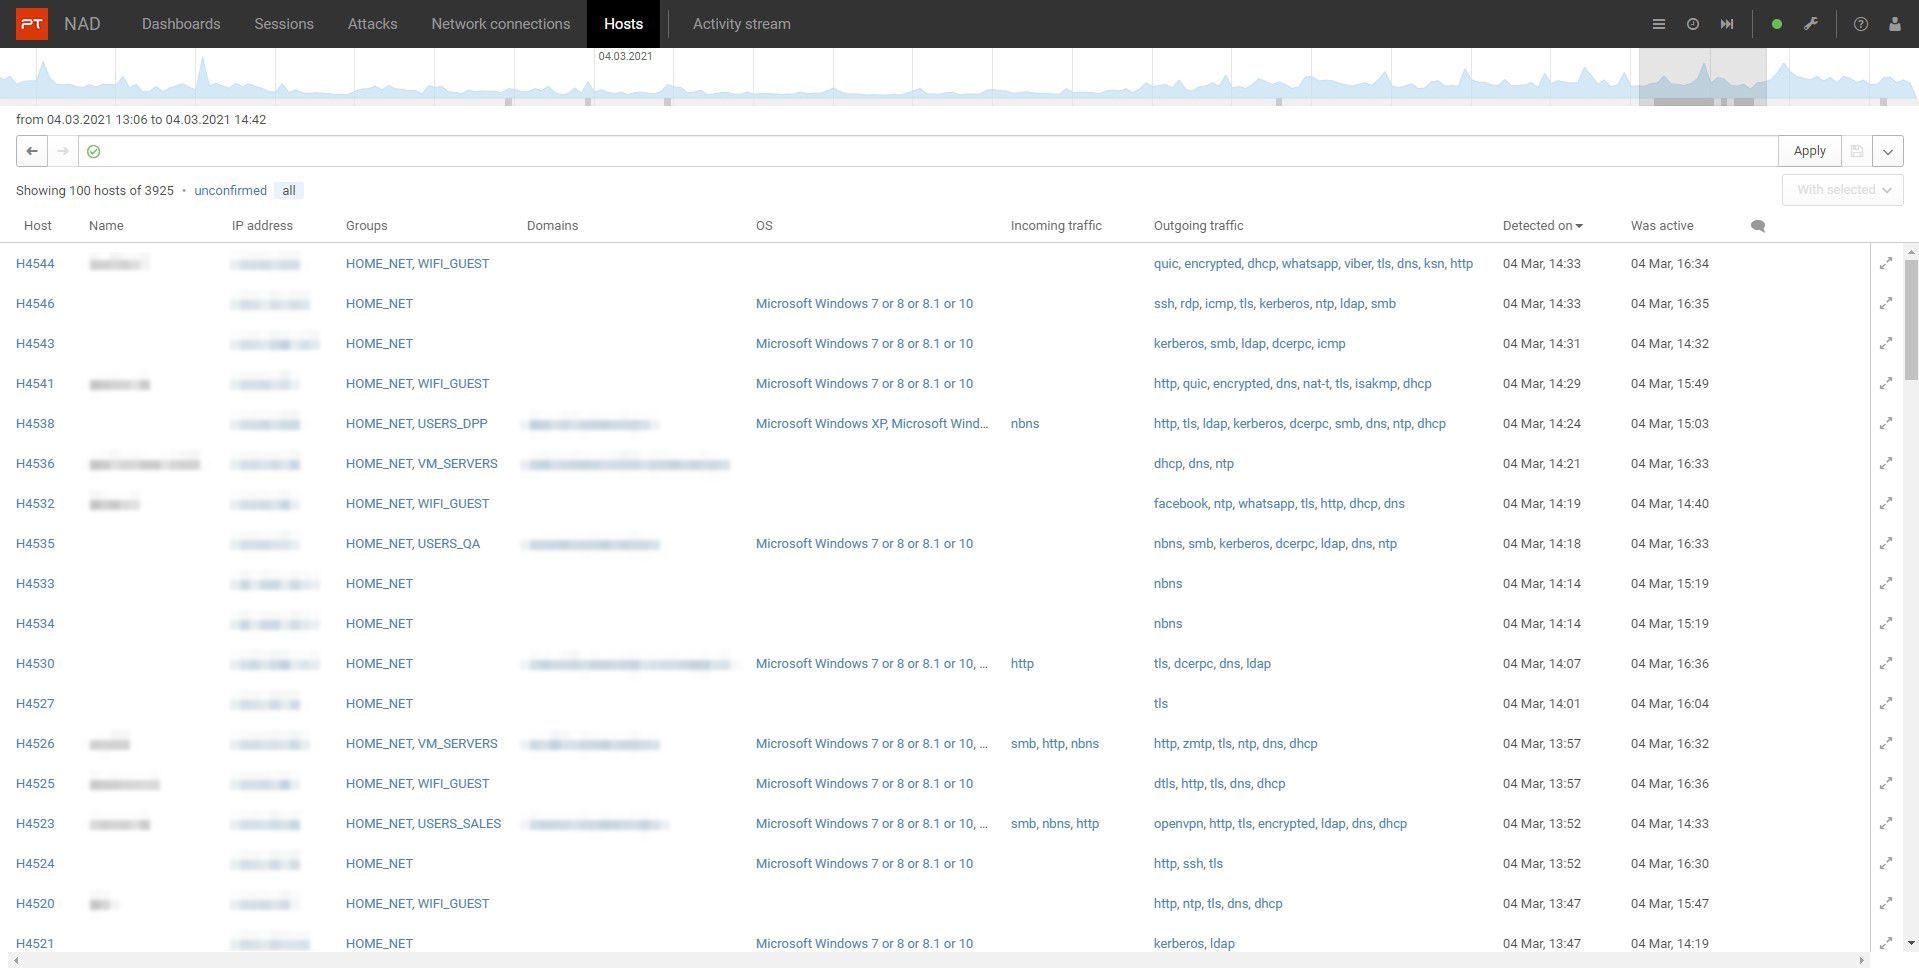
Monitor network hosts
PT NAD users see when a new host appears on the network, as well as an application protocol or the OS has changed. This data can help identify suspicious activity, too.
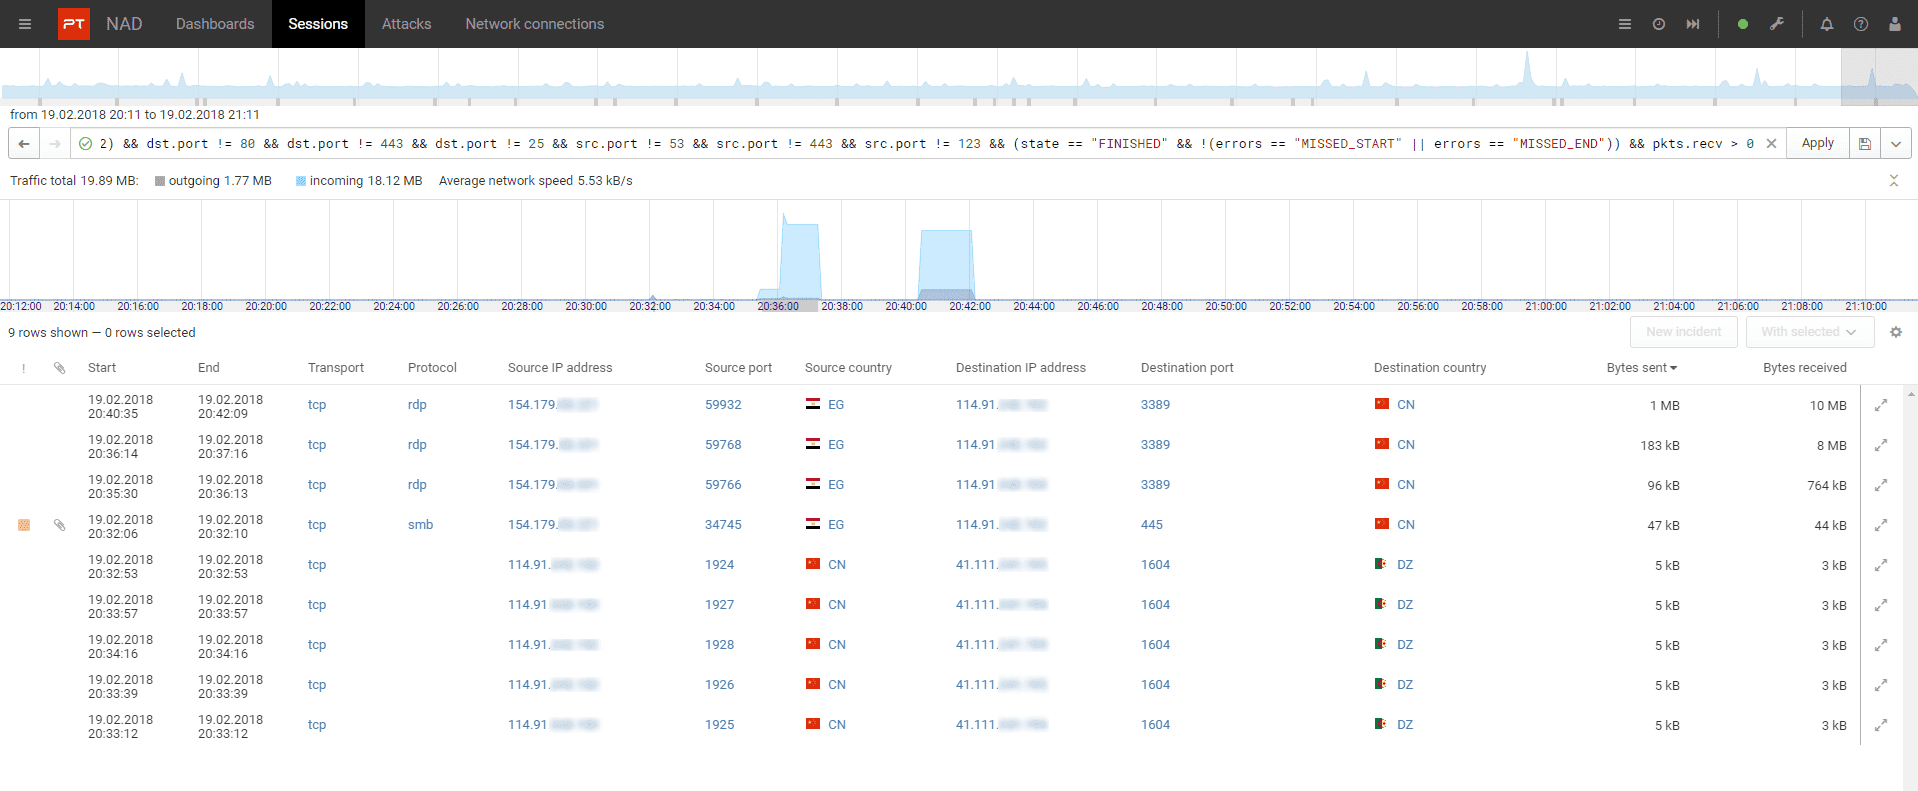
Session filtering
Filtering sessions offers a way to look for malicious activity, indicators of compromise, and configuration errors. PT NAD can quickly sort through sessions by up to 1,200 parameters and display detailed information for each.
Extra materials
Key product information PT NAD brief
Thinking about the best way to protect your company?
Contact us.
During the consultation we'll propose a solution precisely tailored to your organization.