Identifies both traditional file-based attacks and evasive fileless threats, making it effective against complex and previously unknown malware
PT Sandbox
Overview
PT Sandbox is an advanced analysis environment for enterprise defense against APTs and large-scale cyberattacks. It detects sophisticated malware in both files and network traffic while offering extensive customization of virtual environments to improve detection accuracy.
Positive Technologies - a Leader in XDR
Positive Technologies with its comprehensive platform has received strong ratings across technology excellence and customer impact in QKS Group SPARK Matrix.
Use cases
Email protection
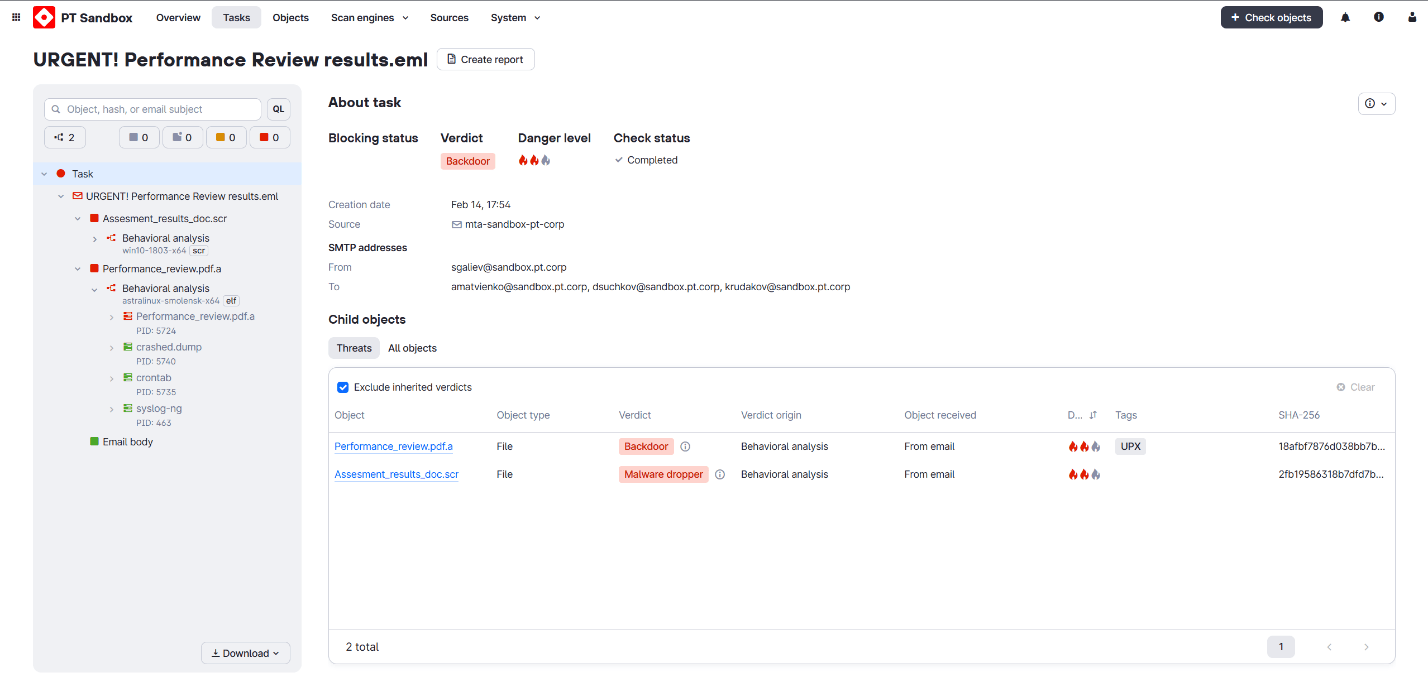
PT Sandbox scans all incoming email traffic at the mail server level, leveraging multiple antivirus engines and YARA rules developed by the PT ESC expert center. Suspicious files and links undergo behavioral analysis in an isolated virtual environment, enhanced by customizable machine learning models. This approach detects unknown, concealed, and obfuscated malware, preventing threats from breaching the corporate perimeter.
Securing file storage and corporate systems
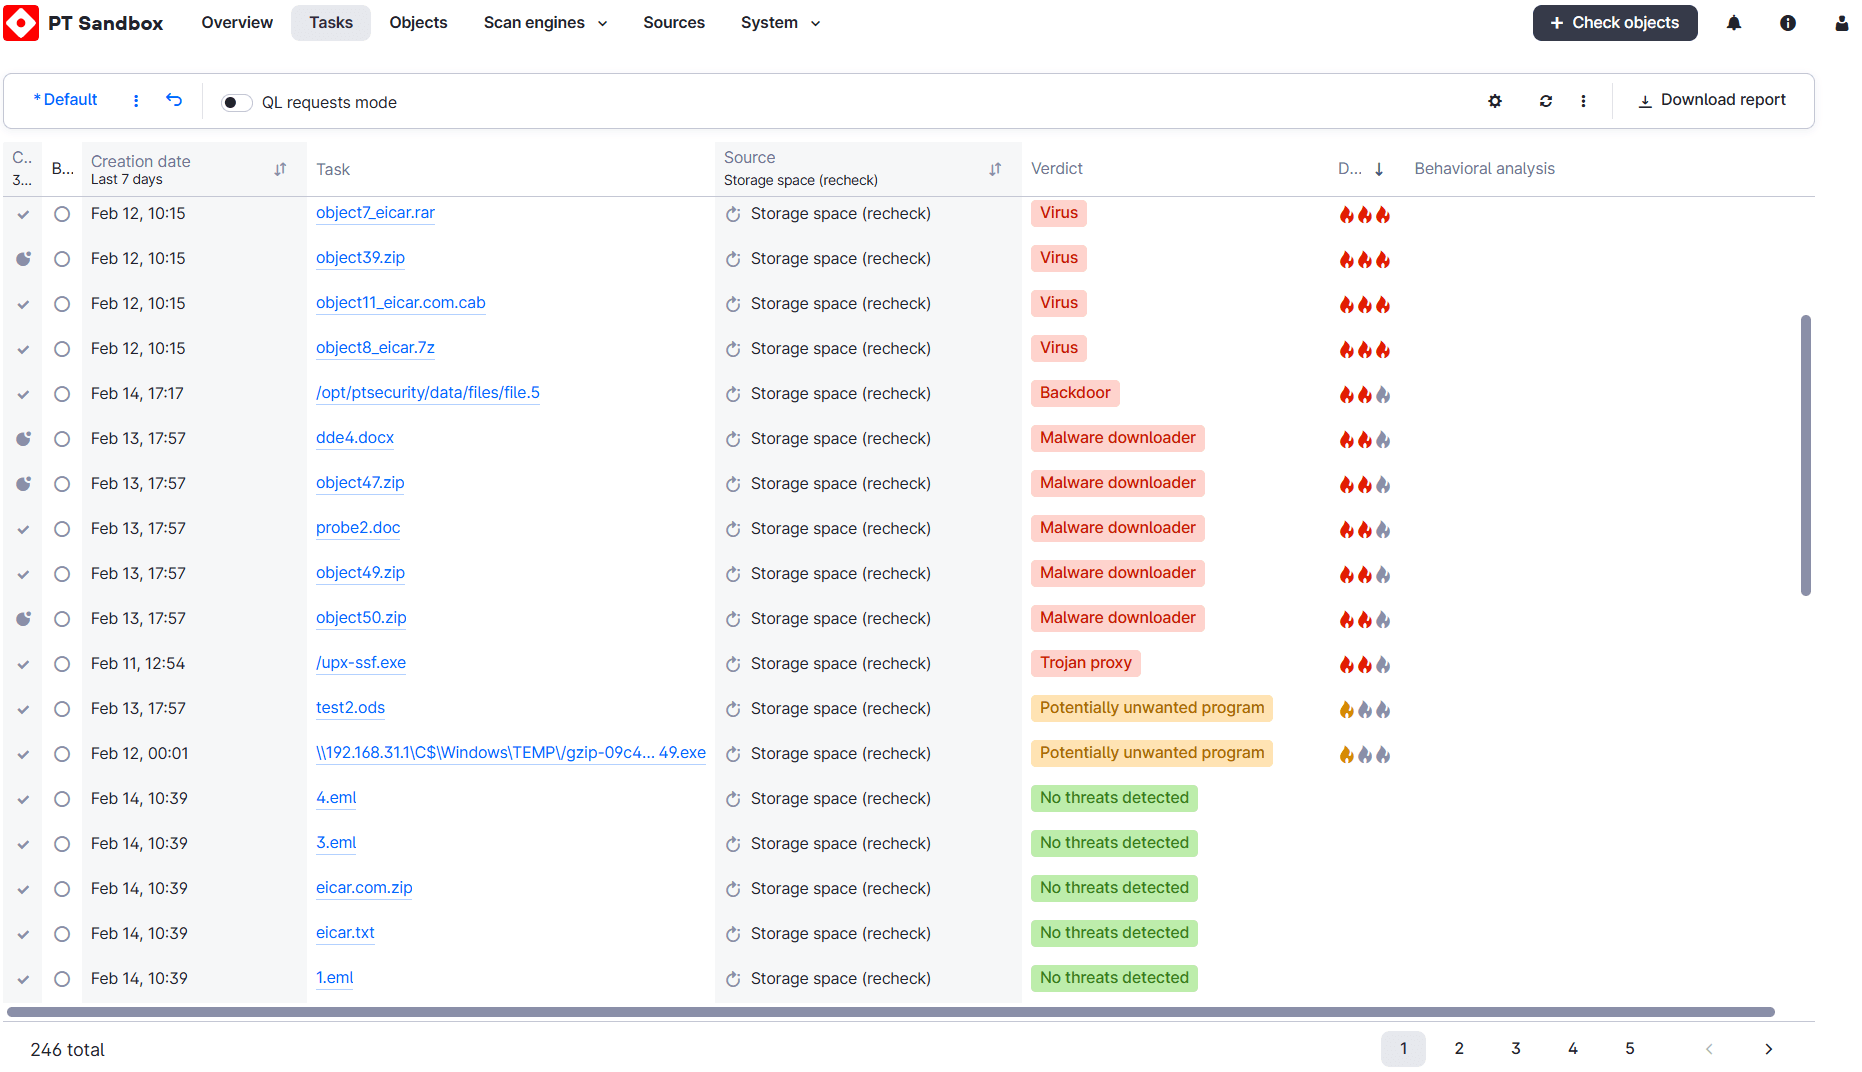
Files are analyzed for threats before they are uploaded to corporate network resources or transmitted through document management systems. This proactive scanning prevents malware from spreading through internal file-sharing and collaboration tools.
Defense against advanced hacking tools
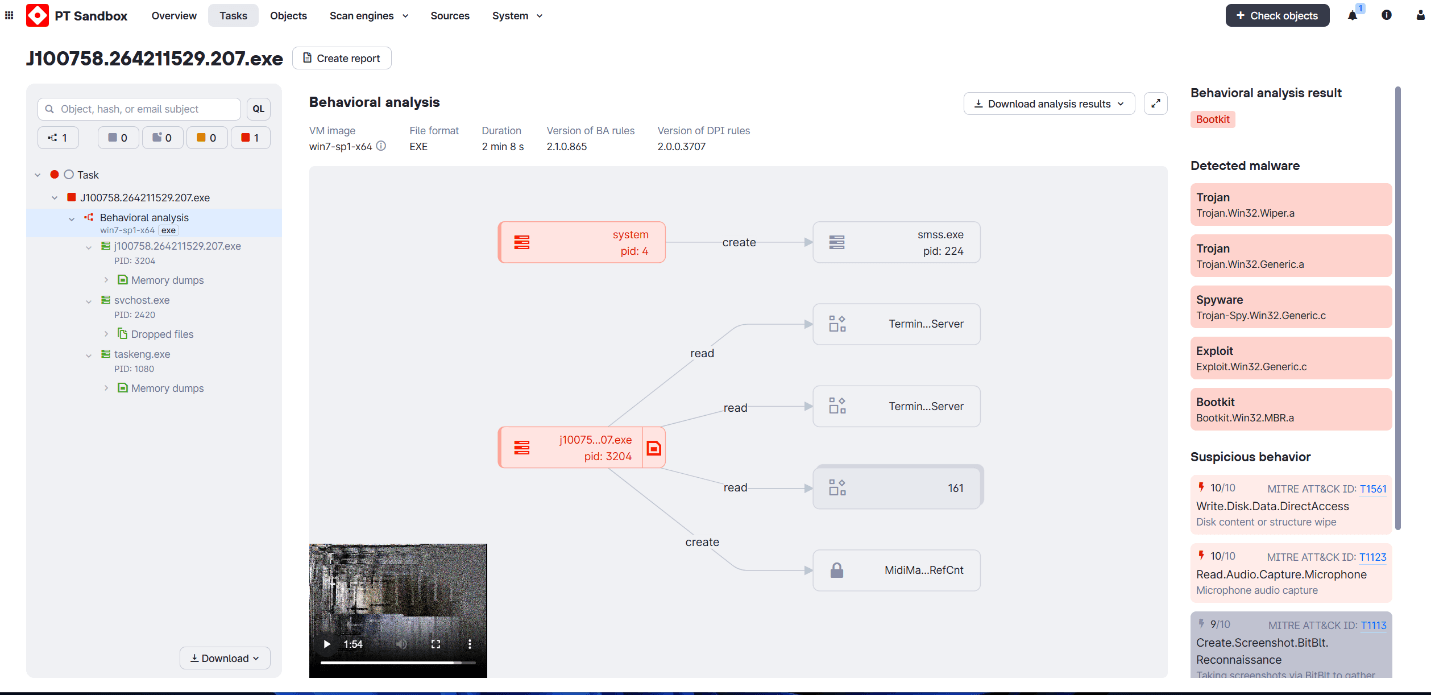
PT Sandbox operates with an architectural advantage, analyzing sophisticated malware at the hypervisor level. Its multi-layered analyzer monitors threats across user space, the OS kernel, and the hypervisor itself. This deep visibility enables detection of both widespread threats and highly evasive malware, including rootkits and bootkits.
Threat hunting and manual sample analysis
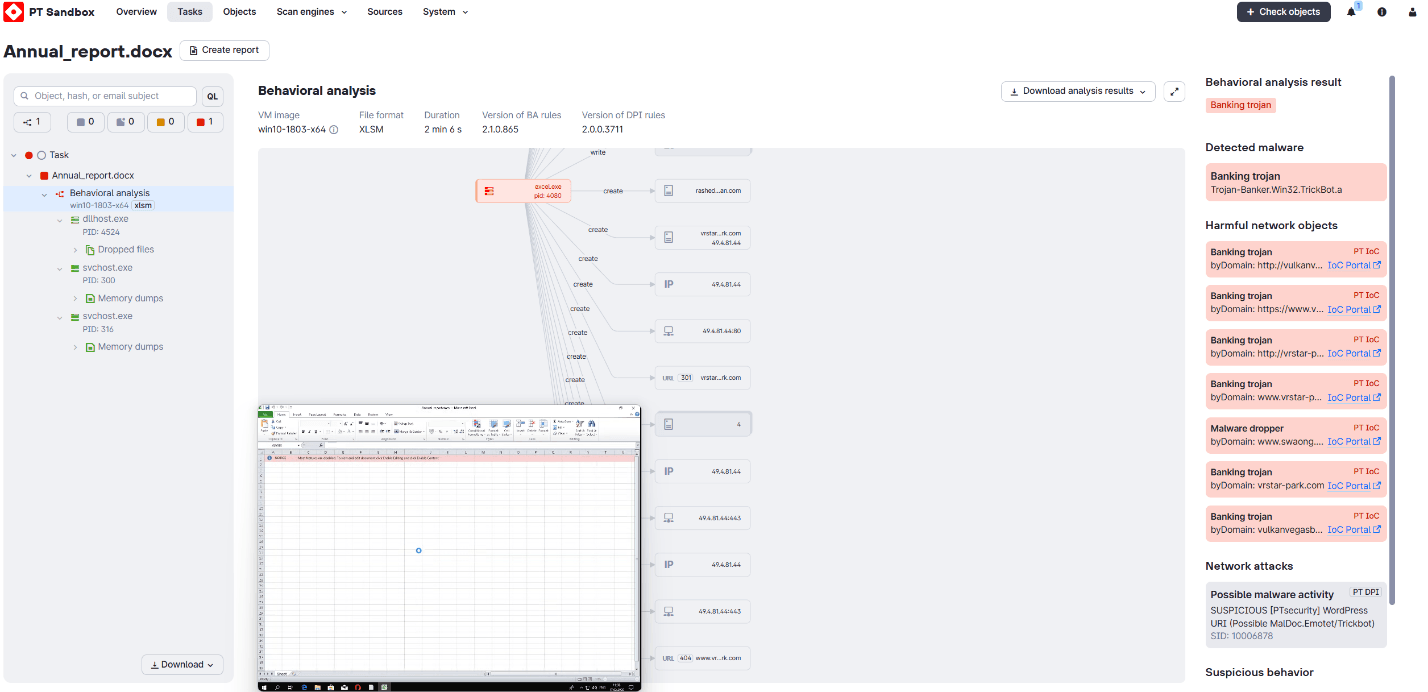
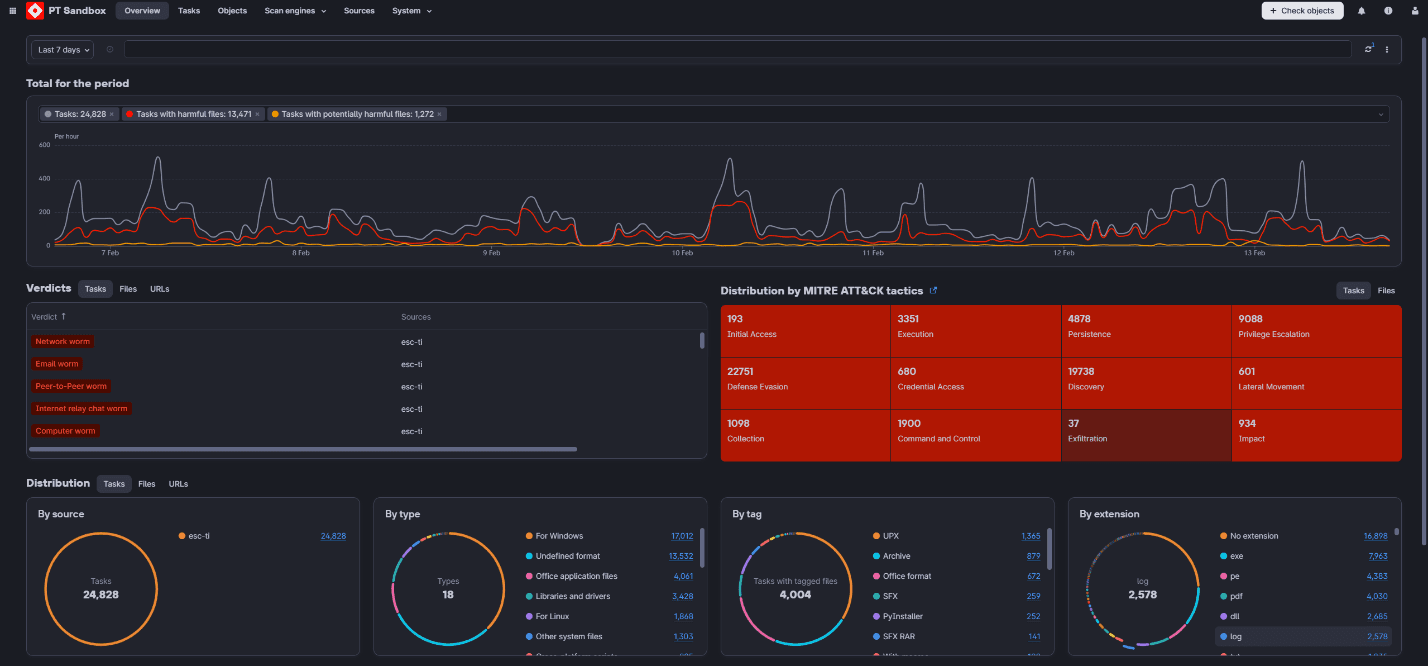
PT Sandbox retains traffic dumps and event data, allowing SOC teams to conduct in-depth analysis of detected malware behavior. It streamlines proactive threat hunting and automates the investigation of suspicious objects found in the infrastructure. The system runs samples across multiple virtual environments, recording all activity and generating detailed behavior graphs and useful artifacts. Analysis results are mapped to the MITRE ATT&CK matrix, enabling rapid mitigation and insight into the attacker's position within the kill chain.
Protection against targeted attacks
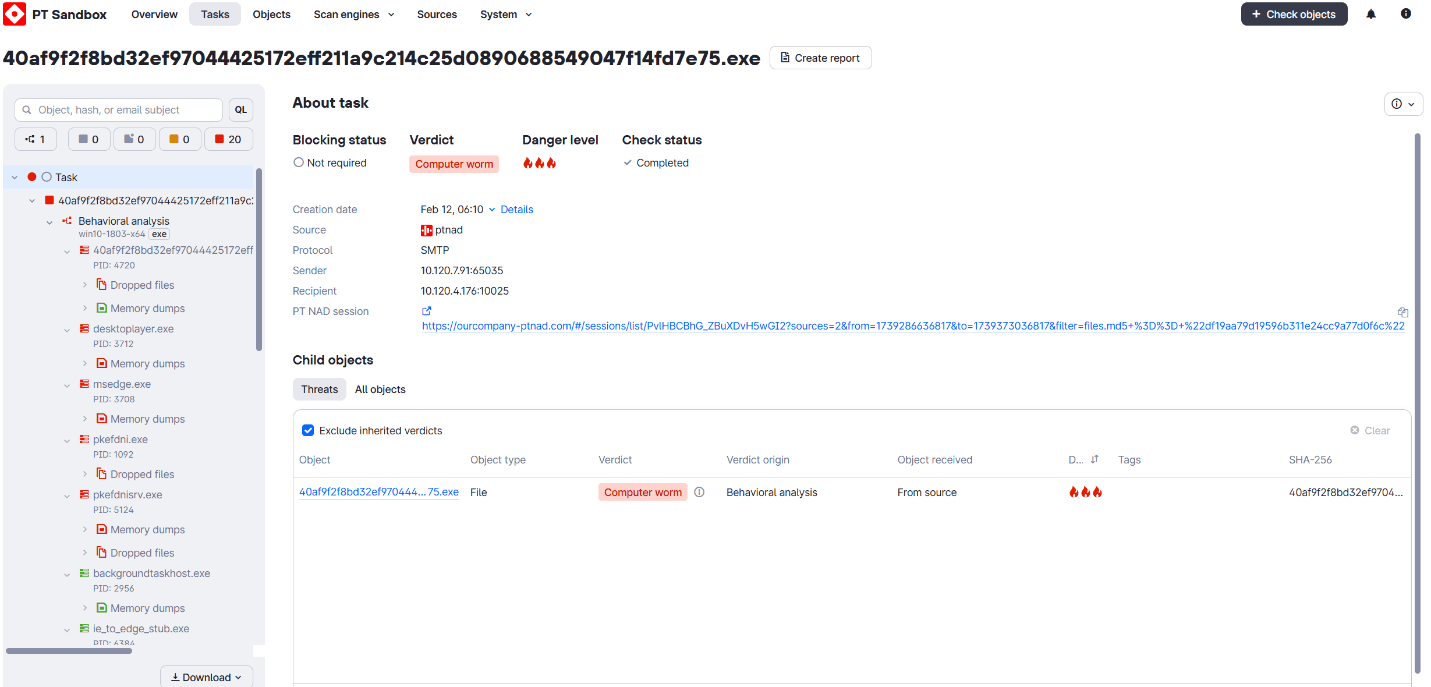
PT Anti-APT is a threat detection suite built on the network traffic behavioral analysis system PT NAD and the network sandbox PT Sandbox. This combination enables detection of targeted attacks both at the perimeter and within the network, reducing the attacker's dwell time.
PT NAD inspects a copy of redirected network traffic for threats. Suspicious files are sent to PT Sandbox, where they undergo behavioral analysis. If malicious content is detected, PT Sandbox delivers its verdict to PT NAD for appropriate action.
Endpoint protection
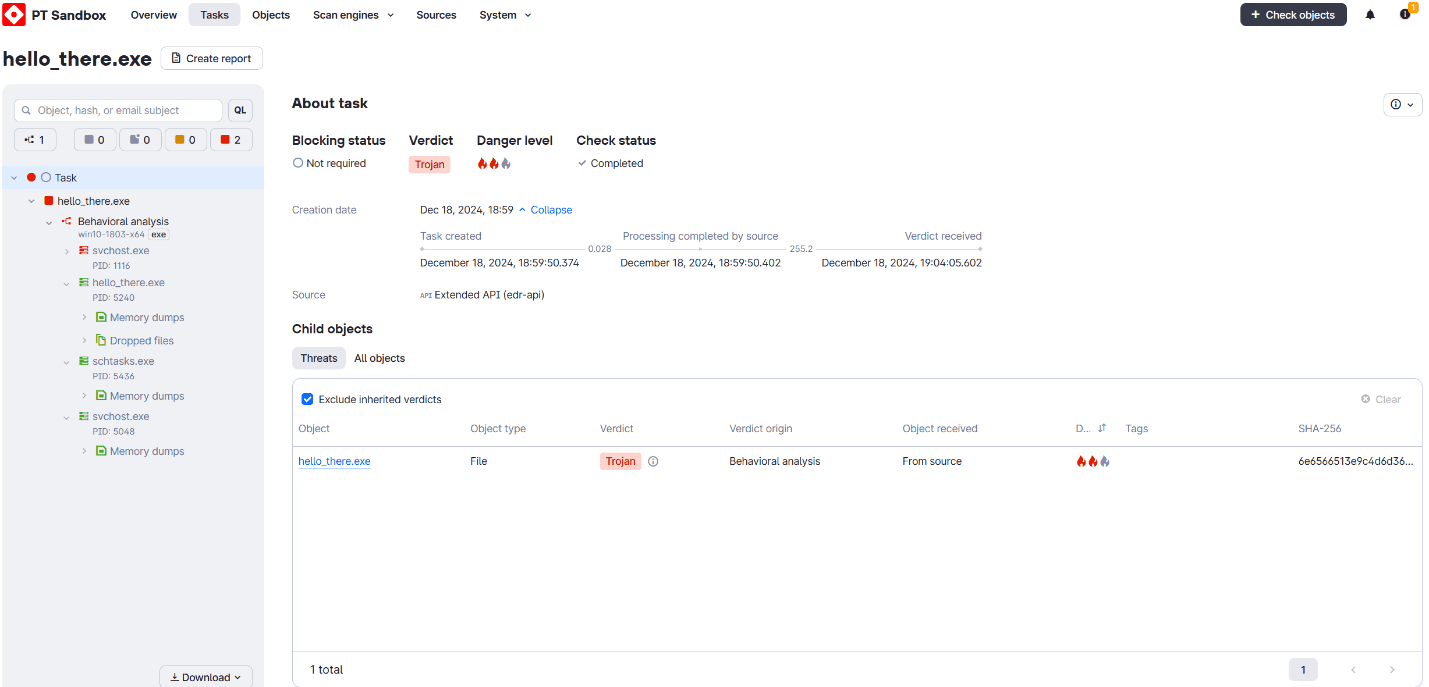
As part of the Positive Technologies XDR solution, PT Sandbox enhances endpoint security by integrating with MaxPatrol EDR. When MaxPatrol EDR detects suspicious files, it sends them to PT Sandbox for analysis. If a threat is confirmed, the system blocks it across all endpoints and relays information about the detected malware to the SIEM system.
Web application protection
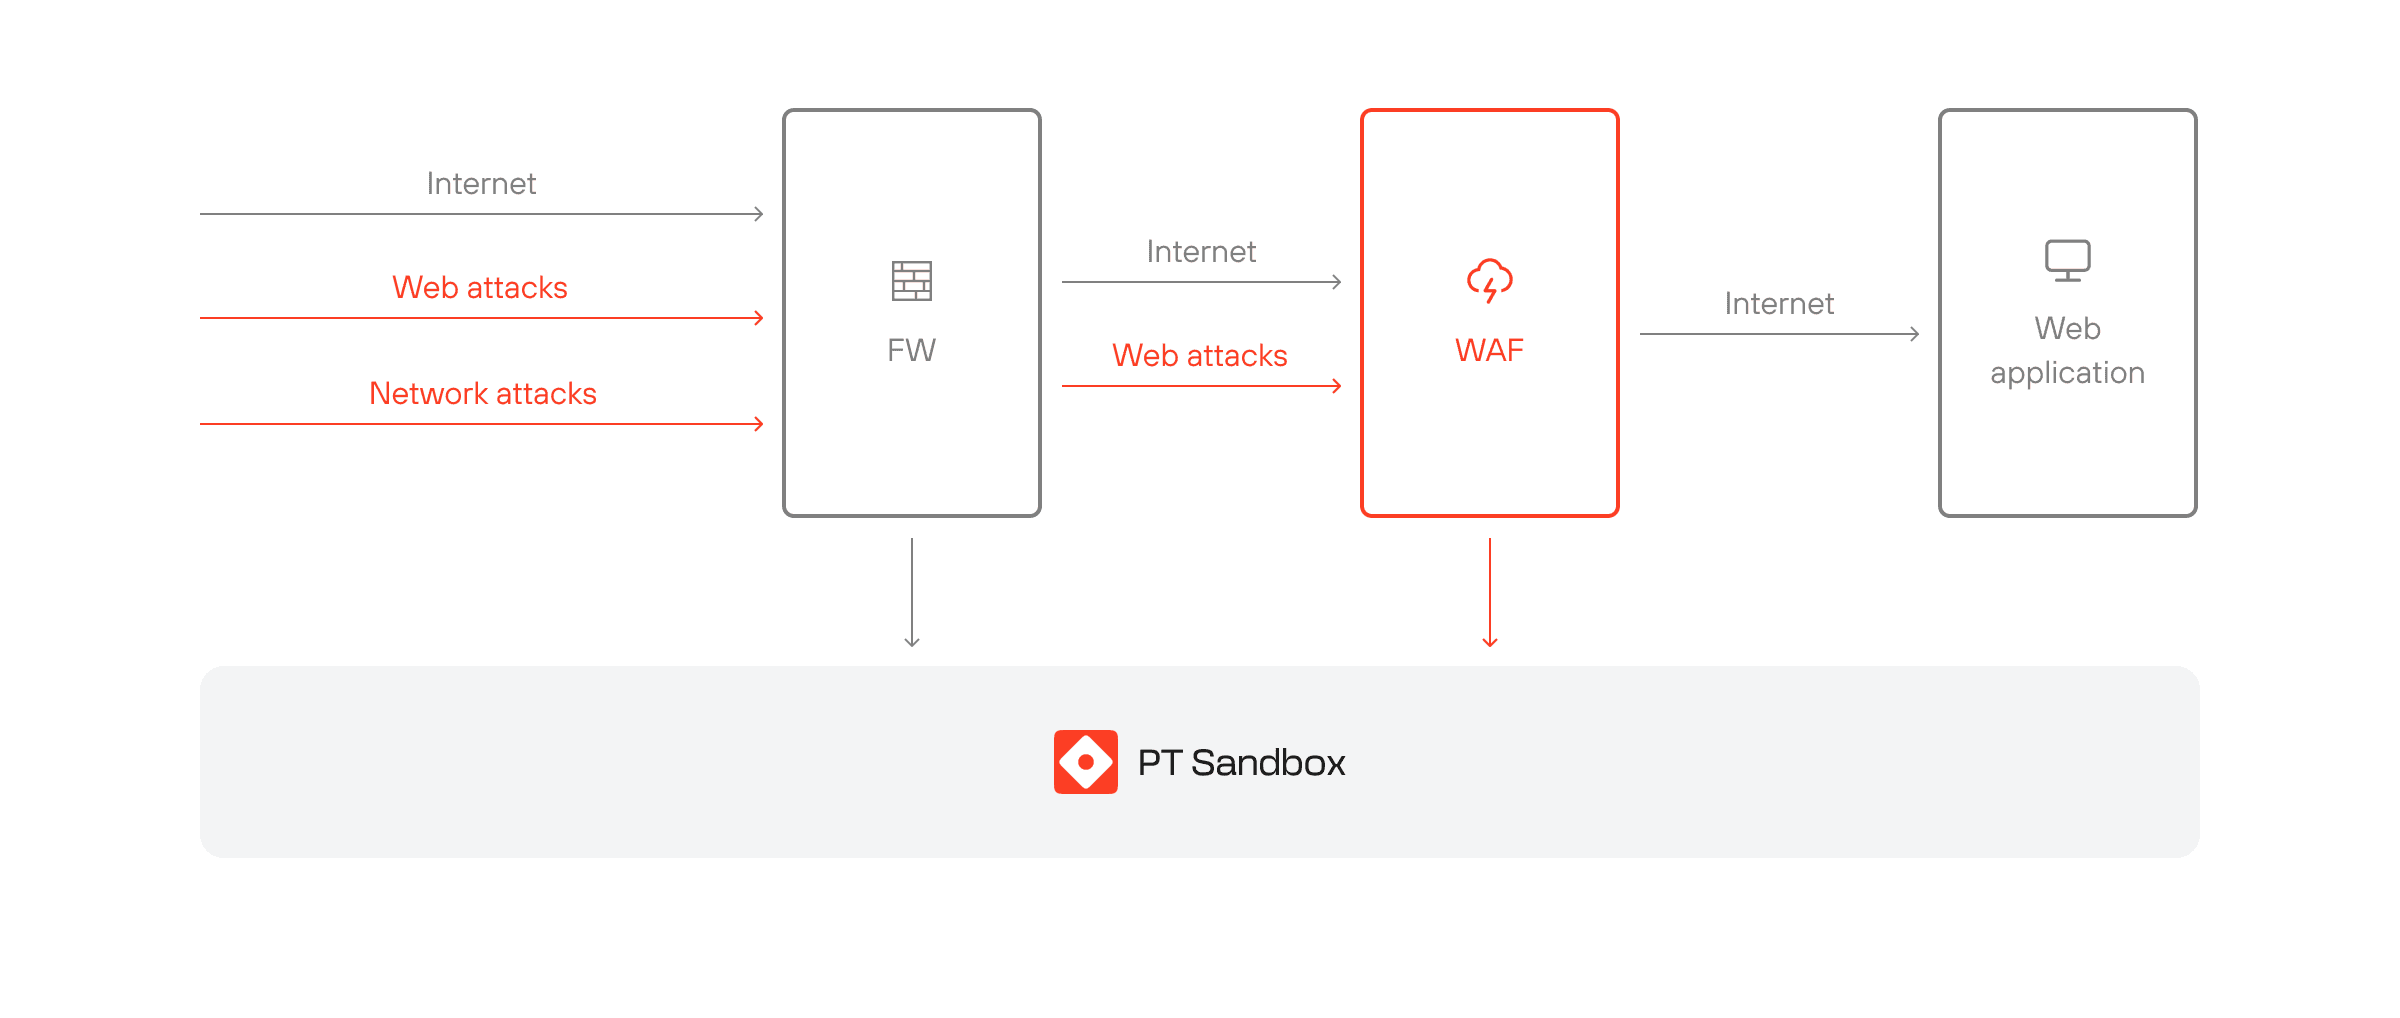
PT Sandbox helps detect supply chain attacks that target a company's customers rather than the company itself. Attackers may exploit vulnerabilities in a web application to replace legitimate files with malicious ones. When integrated with a web application firewall, PT Sandbox analyzes uploaded files, identifies threats, and enables immediate blocking.
Monitoring objects in network traffic
Integration with traffic monitoring and analysis tools allows PT Sandbox to detect and block malware in web traffic, strengthening protection against targeted attacks, advanced malware, and APT threats. It inspects files moving through firewalls and web application firewalls, returning a verdict on whether they contain malicious content.
Securing development repositories
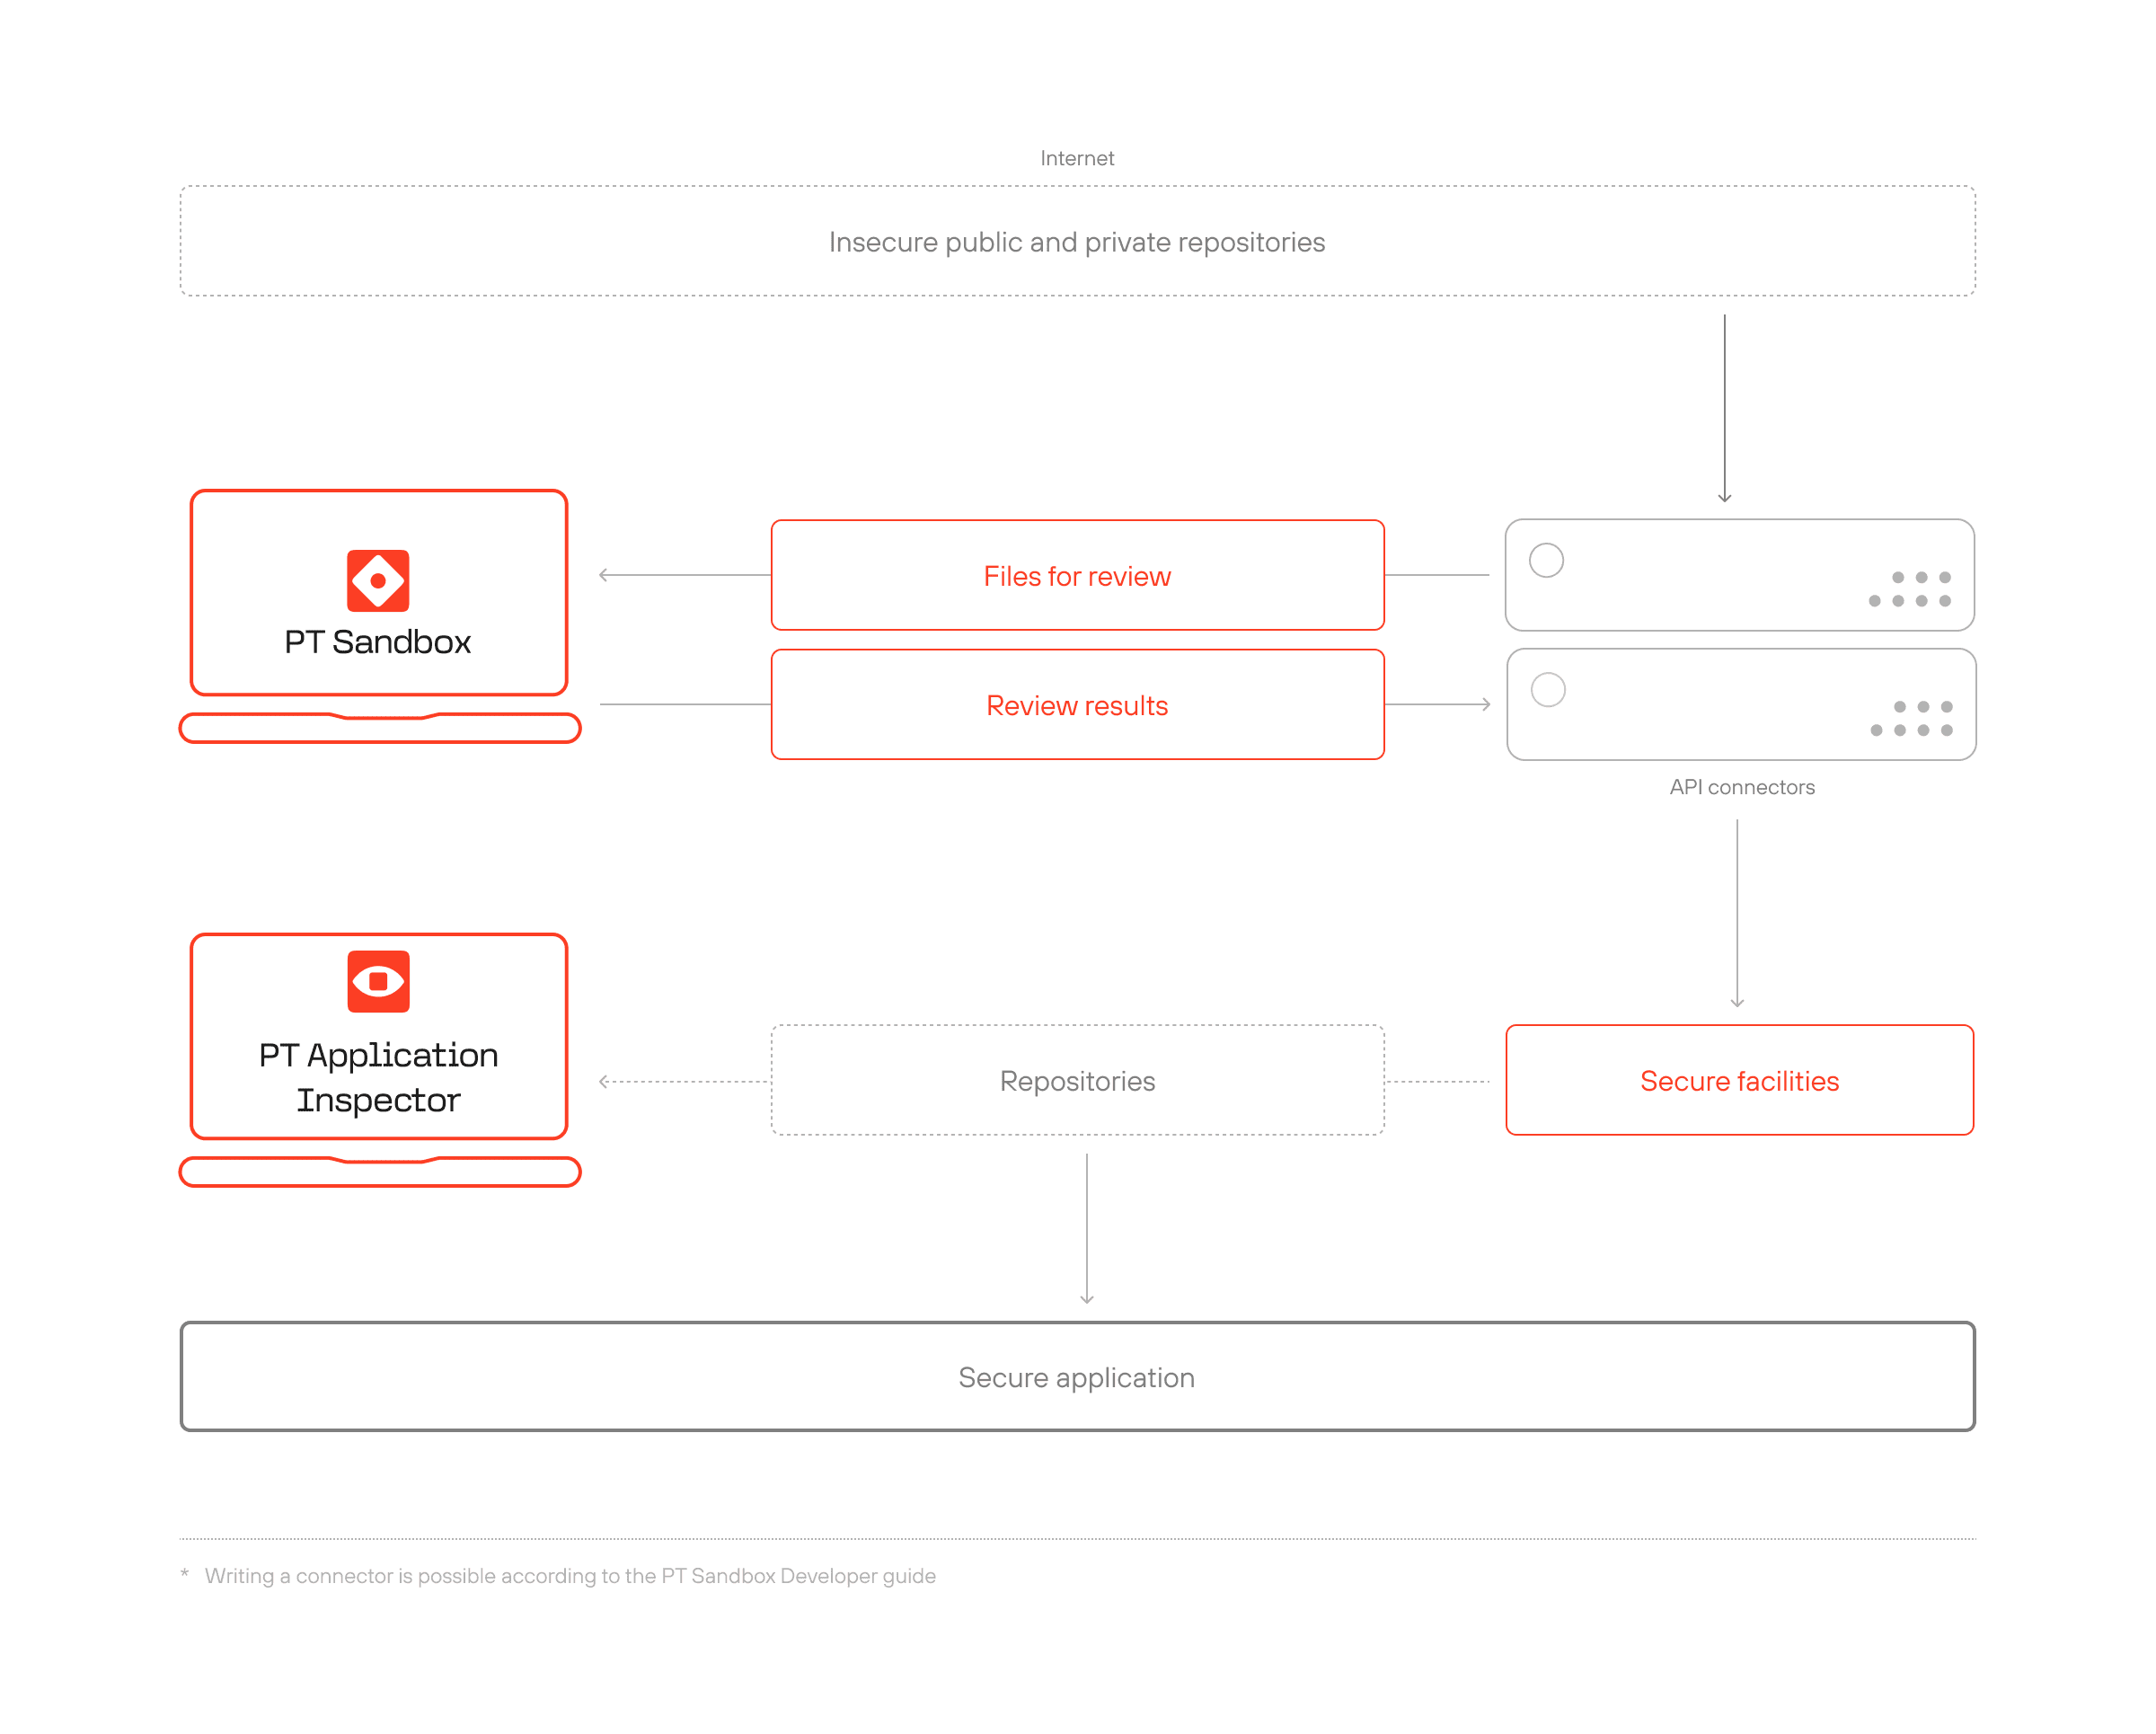
PT Sandbox protects development environments by analyzing applications before deployment. Behavioral analysis of in-house software prevents supply chain compromises, ensuring that published applications do not introduce security risks to users.
Vulnerability protection
Pairing PT Sandbox with MaxPatrol VM strengthens vulnerability management by identifying potential exploits before they can be weaponized. This integration provides an additional layer of security, mitigating risks even for vulnerabilities that have yet to receive official patches.
How it works
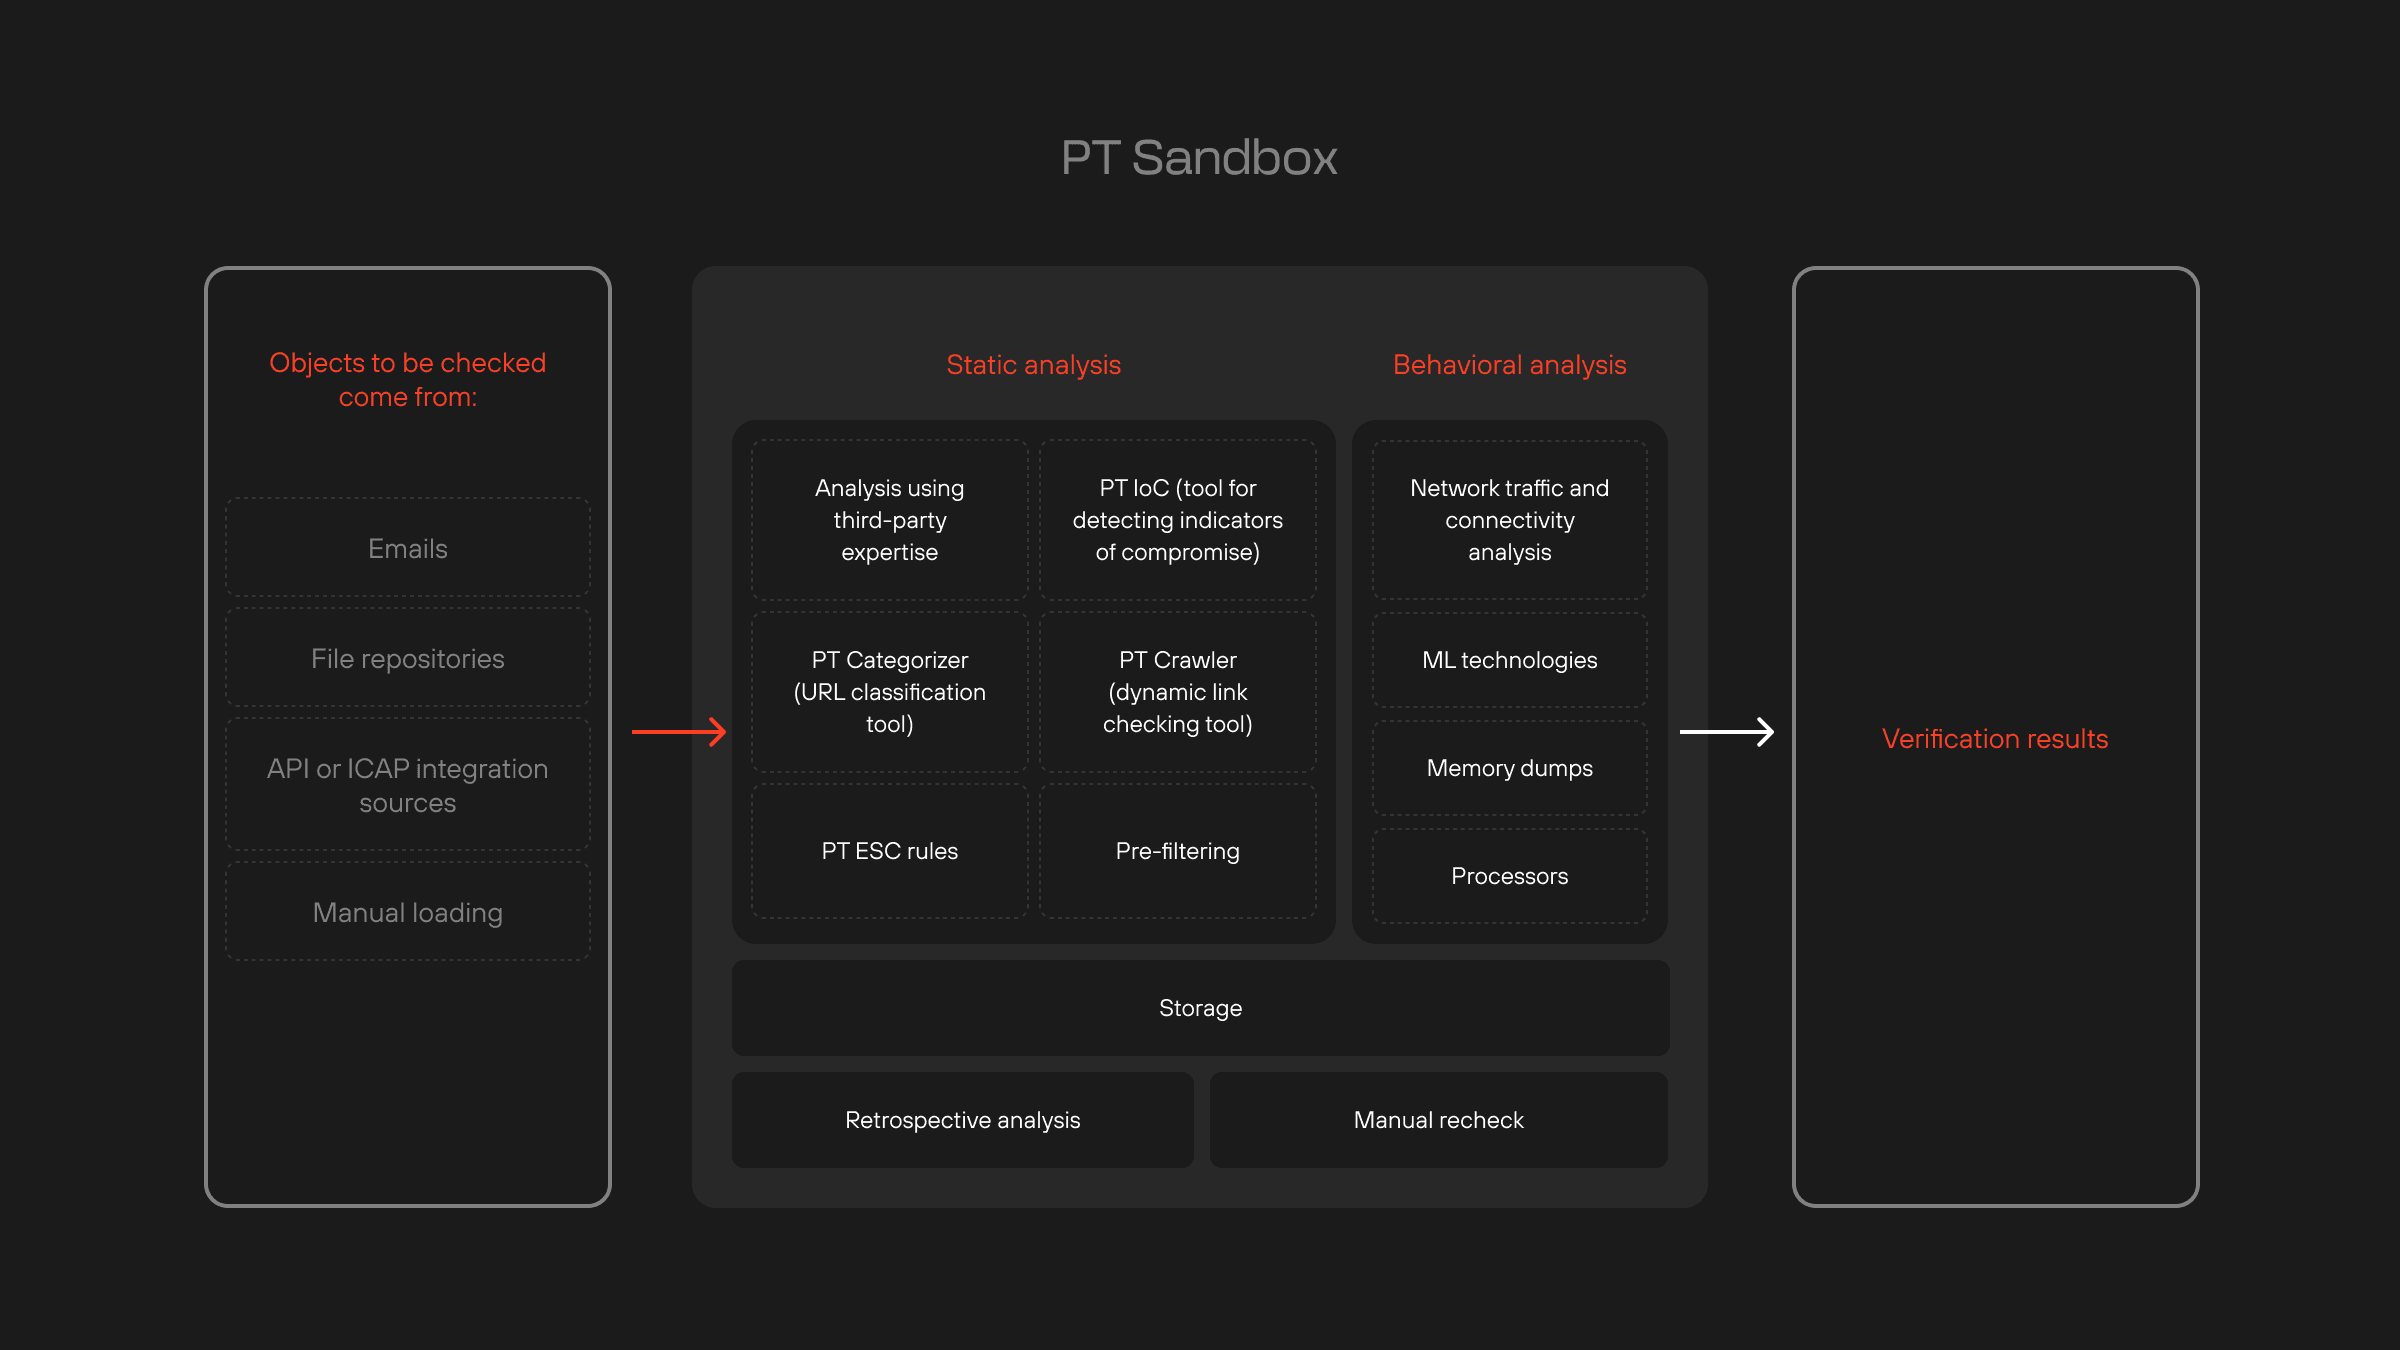
PT Sandbox integrates into the infrastructure, connecting to multiple sources to detect unknown malware and zero-day threats in real time.
ОТ Cybersecurity Framework
Protect your OT environment with Positive Technologies solutions and expertise, aligned with international best practices.
Get a practical guide to designing comprehensive cybersecurity systems and developing OT security management processes based on PT Industrial Cybersecurity Suite.
PT Sandbox advantages
PT Sandbox: AI-powered threat analysis
Customizable machine learning models analyze more than 8,500 behavioral characteristics, including process actions, API call sequences, network activity, and auxiliary object creation. This level of detail enables precise detection of unknown and highly targeted threats.
PT Sandbox expertise
PT Sandbox applies layered detection to uncover malicious activity. Static rules expose fragments of malicious code. Correlation rules track abnormal behavior. Network analysis detects communication with attacker-controlled servers. Machine learning models identify anomalies. OS monitoring sensors catch manipulations that indicate compromise. Every mechanism works in parallel to uncover threats designed to evade traditional security tools.
MITRE ATT&CK coverage
PT Sandbox detects malware tactics and techniques mapped to the MITRE ATT&CK framework for Windows and Linux. It identifies threats at every stage, from execution to persistence, privilege escalation, and lateral movement.
Compatible products
Email remains the primary malware delivery method
Seventy-five percent of cyberattacks begin with an email. Attackers continuously refine malware and develop new evasion techniques, making email security a constant battleground. Regular testing is critical to identifying vulnerabilities before they are exploited.
PT Knockin evaluates the effectiveness of antivirus tools, mail gateways, sandboxes, and other defenses. The service provides actionable recommendations to close security gaps and strengthen protection.
Thinking about the best way to protect your company?
Contact us.
During the consultation we'll propose a solution precisely tailored to your organization.