Autopilot for result-driven cybersecurity
MaxPatrol O2
Intro
MaxPatrol O2 overview
The MaxPatrol O2 metaproduct detects attackers, identifies breached assets, predicts attack scenarios based on company-specific non-tolerable events, and stops attacks before irreparable damage is done.
Result-driven
Rules out non-tolerable events for business.
Automates SOC activities
Reduces the human factor in detection, investigation, and incident response processes, and automates routine actions.
Knows how attackers operate
Utilizes Positive Technologies' unique expertise gained from regular cyberexercises (including Standoff), and bug bounty programs (including Positive dream hunting).
Key features
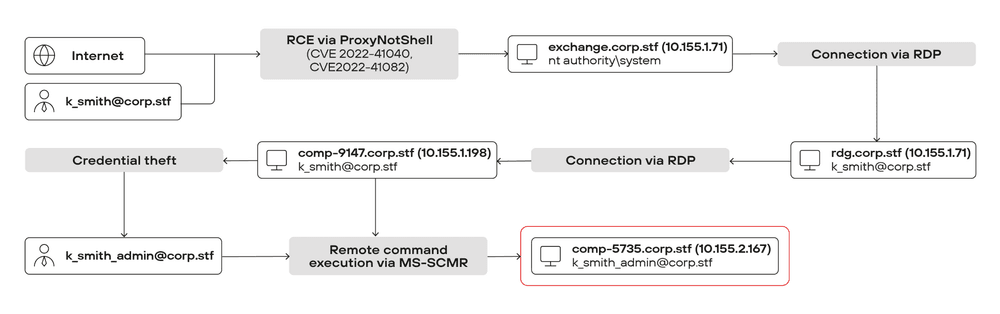
Models potential attacker actions
- Predicts the non-tolerable events that suspicious activity may lead to and how many steps are left until risks are realized.
- Prediction is based on:
- Network reachability of hosts: routing, access lists, NAT rules
- Account permissions for remote login
- RCE vulnerabilities on hosts
- Remote login opportunities through VPN
- Read access to lsass.exe process memory
Detects hacker activity chains
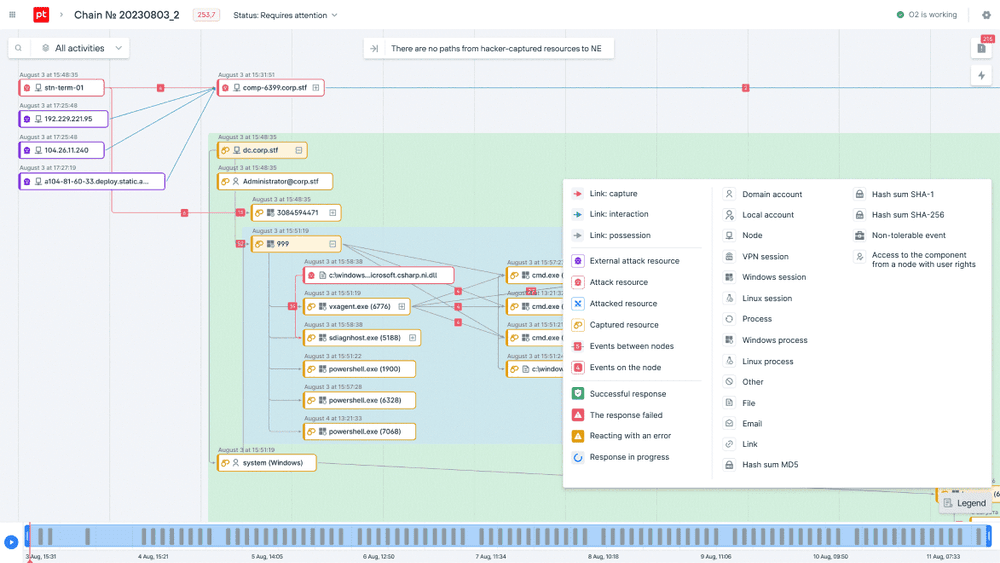
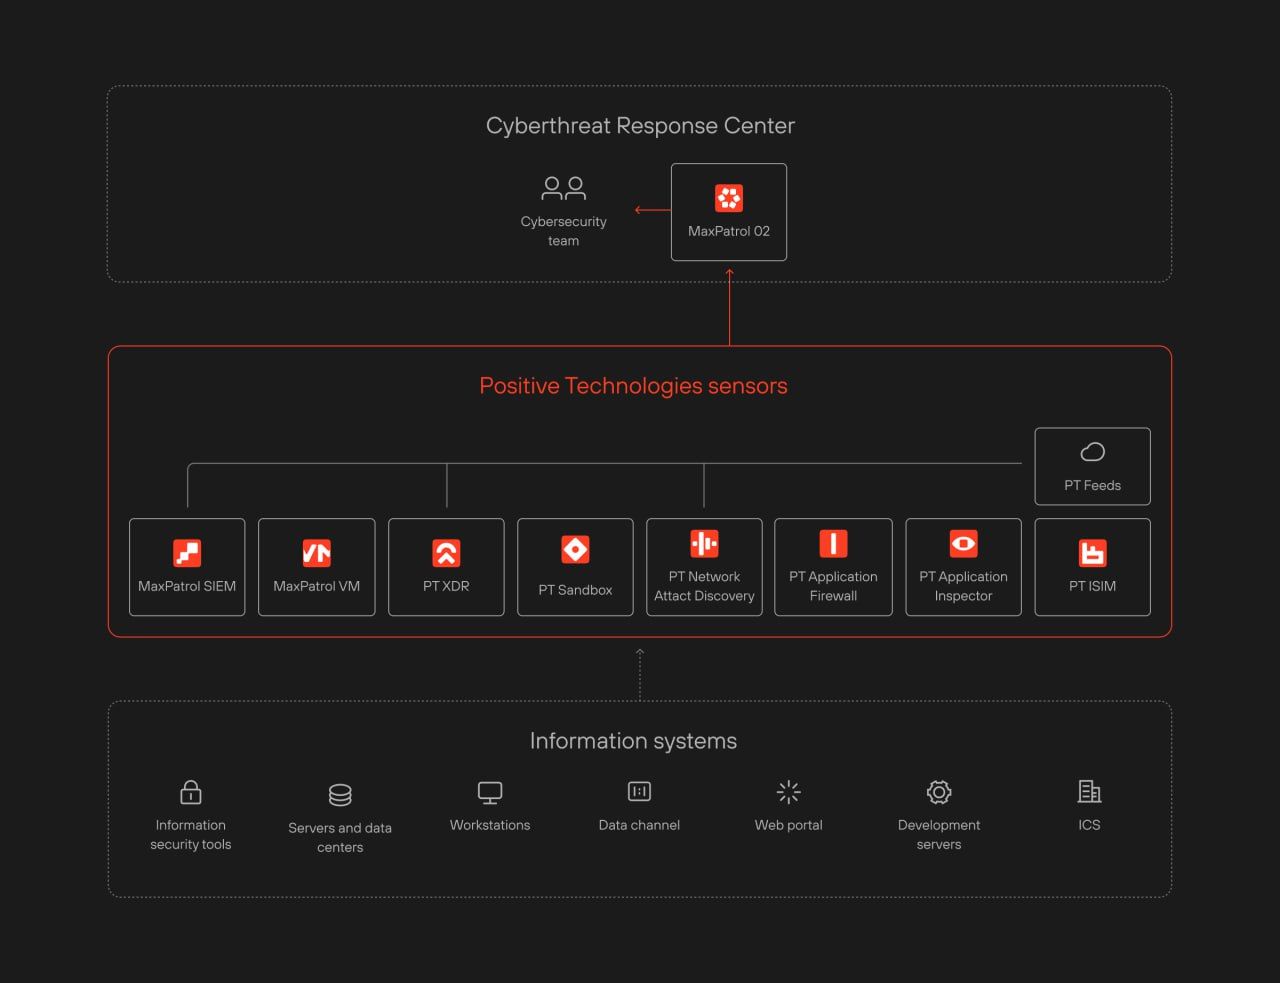
- Analyzes data from Positive Technologies sensors in the metaproduct and demarcates attacking, targeted, and captured resources.
- Correlates resources to build activity chains informed by knowledge of threat actor TPPs.
- Each chain contains a visualization of the attackers' path, plus a prediction of where they will move next.
Automates investigations
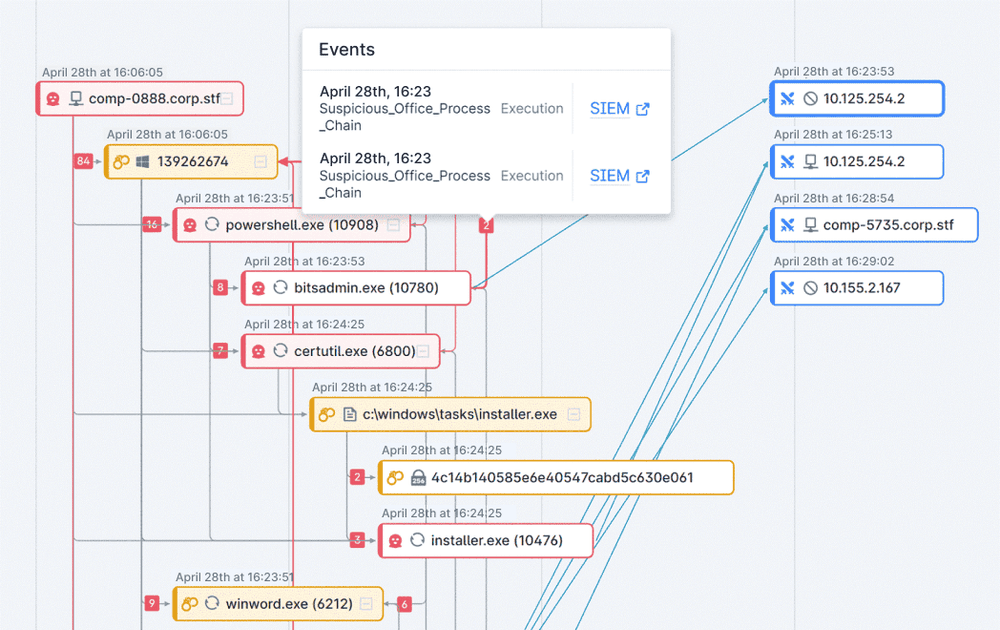
- Uses data from Positive Technologies sensors to build the full attack context and conduct an investigation.
- Obtains enrichment of the following activities:
- Process startup: process -> session -> user
- Remote login: RDP, SMB, WMI
- Movement in the infrastructure: IP -> IP
- VPN session creation: client IP -> external IP + username
Assesses threat severity
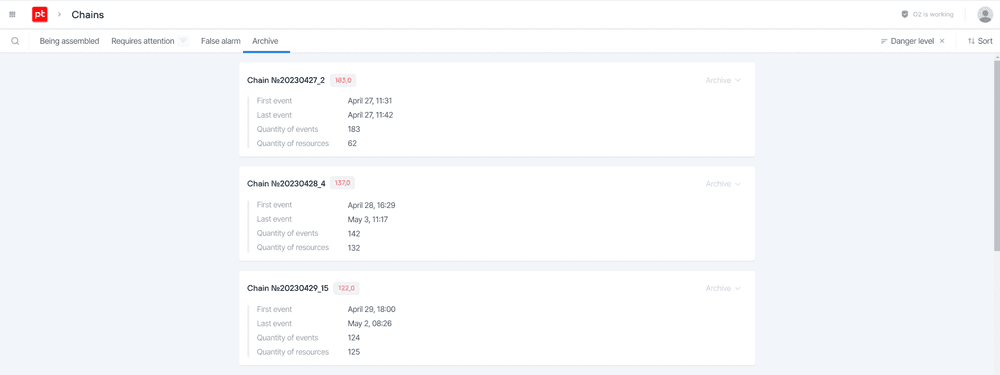
- MaxPatrol O2 views captured resources and assesses the proximity of a non-tolerable event.
Upon receiving this information, the system escalates attack chain status to "Attention required" before stopping the hacker or prompting the operator to make a decision. - The threat severity assessment algorithm continues to improve thanks to regular Positive Technologies cyberexercises and the contributions of Standoff 365 Bug Bounty participants.
Stops attackers
- Considers risks to business processes and suggests the optimal response scenario.
The scenario can be implemented automatically or manually if adjustments are needed. - Possible response actions:
- Lock account: in the domain or locally, in Windows, Linux, or Mac.
- Block IP address in the firewall: incoming/outgoing traffic.
- Isolate host on the network.
- Stop running process.
- Revoke OpenVPN token.
- Delete email message.
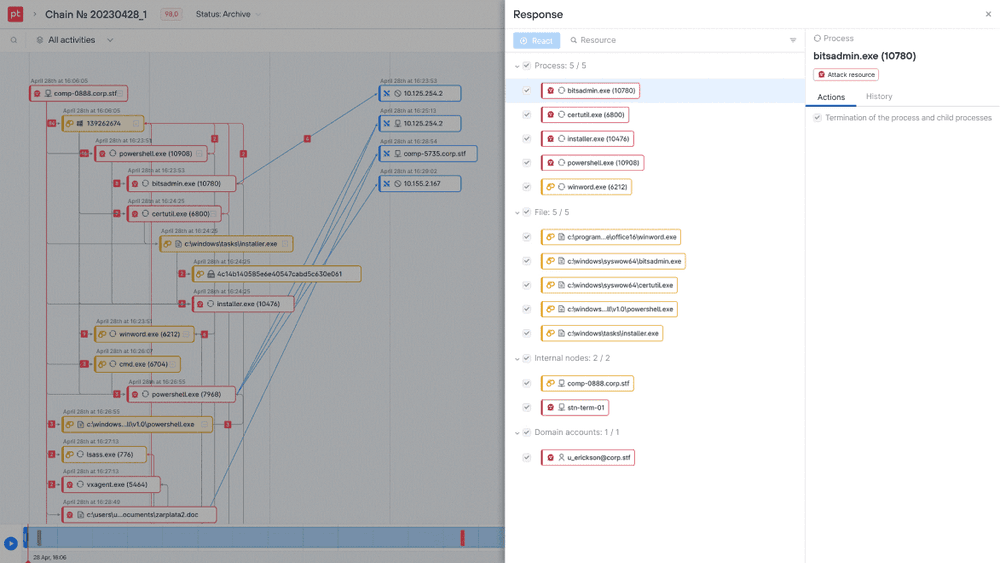
How the metaproduct works
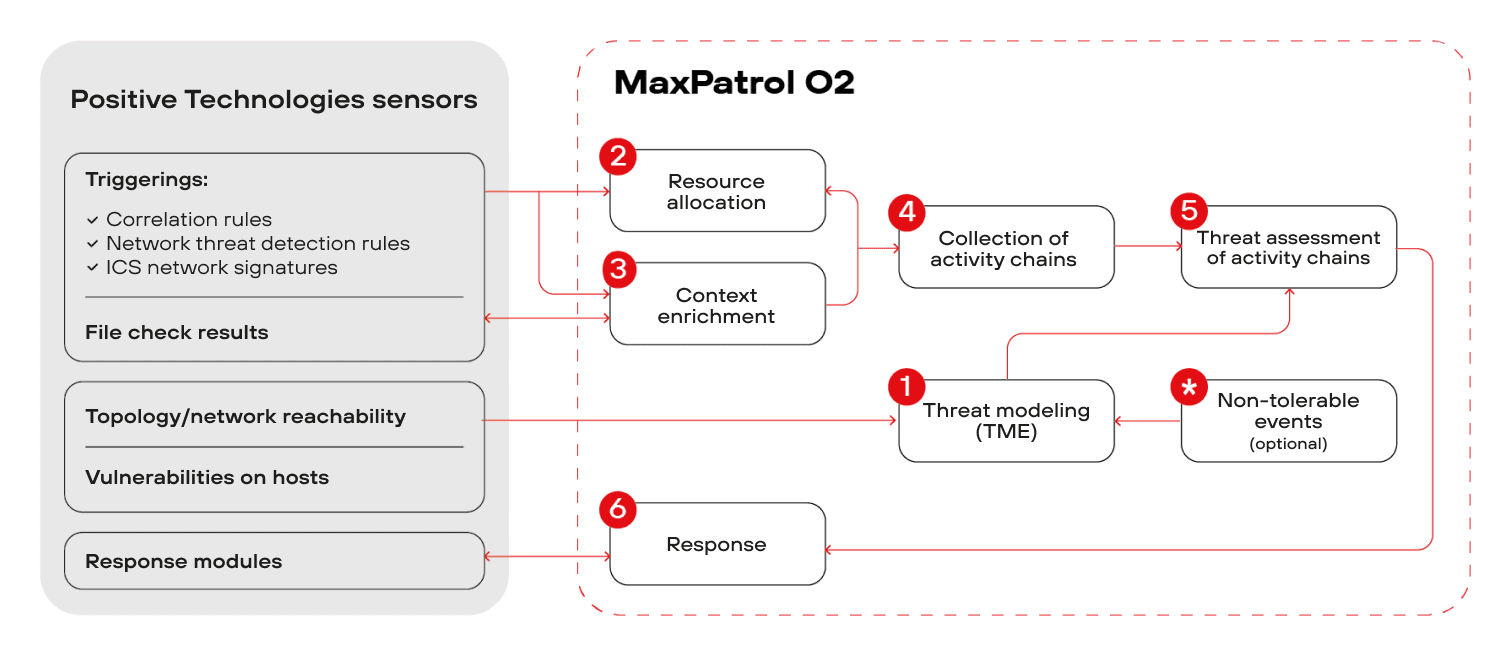
MaxPatrol O2 benefits
Interaction scheme
Thinking about the best way to protect your company?
Contact us.
During the consultation we'll propose a solution precisely tailored to your organization.